Enterprise Blockchain: Use Cases, Platforms & Adoption
Most enterprise blockchain pilots still stall before production. This guide names the projects that are actually live in 2026 and the ones that were shut down, compares the platforms worth evaluating, and shows how to scope a proof of concept that has a real chance of shipping.

On this page

Enterprise blockchain is a permissioned, shared ledger that lets separate organizations agree on one set of records without any of them owning the master copy. In 2026 that idea takes three forms running side by side: private consortium networks built for banks and supply chains, enterprise access controls layered onto public chains, and regulated institutions settling tokenised assets at production scale. These used to get pitched as competing bets on "the future of blockchain." They are now different tools for different jobs, picked the way you'd pick between a relational database and a data warehouse: based on the problem, not the hype cycle.
That distinction matters because the last three years separated the enterprise blockchain projects that work from the ones that were always a science-fair demo. JPMorgan's Kinexys platform has processed over $4 trillion since inception. Maersk and IBM shut TradeLens down in 2023. Both are true at once, and neither tells you what the technology is actually good for. This guide names the projects still running and the ones that were discontinued, compares the platforms worth evaluating, and shows how to scope a proof of concept with a real chance of reaching production.
The short version
- Enterprise blockchain in 2026 spans permissioned consortium networks, enterprise controls layered onto public chains, and banks settling tokenised assets directly on public layer-2s such as Polygon.
- Live and growing: JPMorgan's Kinexys (over $4 trillion processed since inception, September 2026), Broadridge's Distributed Ledger Repo ($357 billion in average daily volume, June 2026), and the Canton Network (31 founding institutions including Goldman Sachs and BNP Paribas).
- Shut down: Maersk and IBM discontinued TradeLens in 2023, and the 12-bank we.trade consortium became insolvent in 2022, both because not enough independent organizations ever put real data on the shared ledger.
- It only pays off when several organizations must agree on one record and no single one should own it. When one company controls the data, a database is faster and cheaper, which is why our own supply-chain product runs on one, not a chain.
- Most production deployments are permissioned or hybrid, not fully public: private logic anchored to a public chain, or run directly on a public layer-2 like Polygon under enterprise-grade access controls.
- A pilot only becomes a production system when the consortium commits before the platform gets chosen. That ordering, not the technology, decides most outcomes.
What enterprise blockchain means in 2026
Enterprise blockchain is a permissioned, shared ledger that a known group of organizations use to agree on one record, instead of each running its own copy and reconciling by hand. In 2026 it shows up in three shapes.
First, the classic permissioned or consortium network: a private ledger where every participant is a vetted, identified organization, there is no public token, and membership is controlled by legal agreement. Hyperledger Fabric, R3 Corda, and private EVM chains all fit this shape, still the default for bank consortia and supply-chain networks.
Second, and newer, easy to miss: enterprise-grade access control layered directly onto a public chain, rather than a private copy of the ledger. A regulated institution transacts on a public network like Polygon or Ethereum, with permissioning enforced at the application layer, allowlists, transfer restrictions, role checks, instead of at the network layer. KfW and DZ BANK used exactly this on 25 March 2026, mapping the full lifecycle of a digital bond, issuance through settlement, on the public Polygon blockchain, with Germany's Bundesbank providing the settlement interface. Settlement took about an hour, against roughly five days for a conventional bond issuance.
Third, a bank settling tokenised assets directly, at institutional scale, sometimes on infrastructure it built itself. JPMorgan's Kinexys platform, renamed from Onyx in November 2024, settles institutional payments and tokenised deposits and had processed over $4 trillion since inception as of 2 September 2026. HSBC's Orion has issued more than $3.5 billion in digitally native bonds and was awarded the mandate for the UK's first tokenised sovereign bond pilot.
None of these three enterprise blockchain shapes is more real than the others. A consortium network solves multi-party reconciliation, a permissioned layer on a public chain solves independent verifiability without running your own network, and direct institutional settlement solves the cost and speed of moving regulated assets. What they share is the permissioned part: a record several parties can trust without one of them controlling it.
Enterprise blockchain projects that are actually live
The state of enterprise blockchain in 2026 isn't a story about hype fading. It's a story about a handful of platforms reaching real institutional scale while several well-funded consortiums shut their doors.
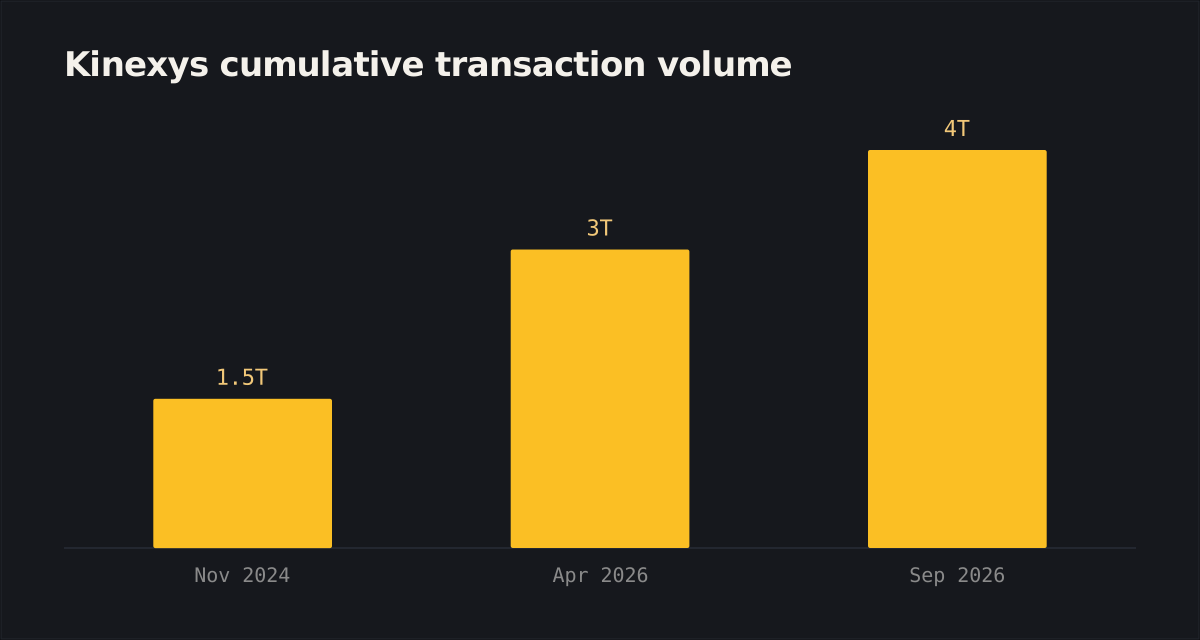
The three points are JPMorgan's own figures: "$1.5+ trillion" on the Introducing Kinexys page of 6 November 2024, "more than $3 trillion in transactions since inception and averaging more than $5 billion daily" in the Kinexys 2026 milestones announcement of 28 April 2026, and the $4 trillion figure in the September 2026 newsroom release cited above.
Three patterns explain almost every row below. The platforms that reached scale are owned by one large institution able to drive adoption across its own network (JPMorgan, Broadridge, HSBC), not a voluntary consortium hoping enough competitors show up. The ones that failed needed dozens of independent organizations to agree to share data and never got there. And the newest entrants, Visa and Mastercard, extend existing payment rails onto blockchain infrastructure rather than asking anyone to adopt something unfamiliar.
Three rows reward a closer look. SWIFT's shared ledger only reached a real pilot with named banks (Citi, HSBC, UBS, BNP Paribas, Standard Chartered, Wells Fargo, BNY, DBS, and MUFG among them) on 9 July 2026, years after most observers had stopped guessing whether SWIFT would move at all. Canton Network's 31 founders included direct competitors, Goldman Sachs alongside BNP Paribas and Deutsche Börse, the exact coordination problem that sank we.trade; the difference is that Canton's privacy model lets rivals transact without exposing positions to each other. And IBM Food Trust is the surprise entry: contrary to the assumption that IBM's blockchain bets all died with TradeLens, its documentation was still being updated as of July 2026, with no record of a sale or wind-down.
Where enterprise blockchain earns its place, and where a database wins
Enterprise blockchain earns its place in exactly one situation: several organizations need to agree on the same record, and no single one of them should own it. Run every candidate use case through that test before anything else.

We've built on both sides of that line ourselves. Our own HaulBreeze supply-chain platform runs on one unified data layer, not a distributed ledger, because Idealogic is the sole owner of that system and there's no multi-party trust problem to solve. Chaindoc, by contrast, writes a hash of every signed document on-chain, because a regulated business shouldn't have to take the platform's own word for it. Same test, opposite answer, both correct for the problem in front of them. More on both further down.
Permissioned vs public vs hybrid: how enterprises deploy blockchain
For most enterprise blockchain deployments the default is still a permissioned chain, but "public versus permissioned" is no longer a clean binary. It comes down to three things: privacy, performance, and how independently the record needs to be verifiable.
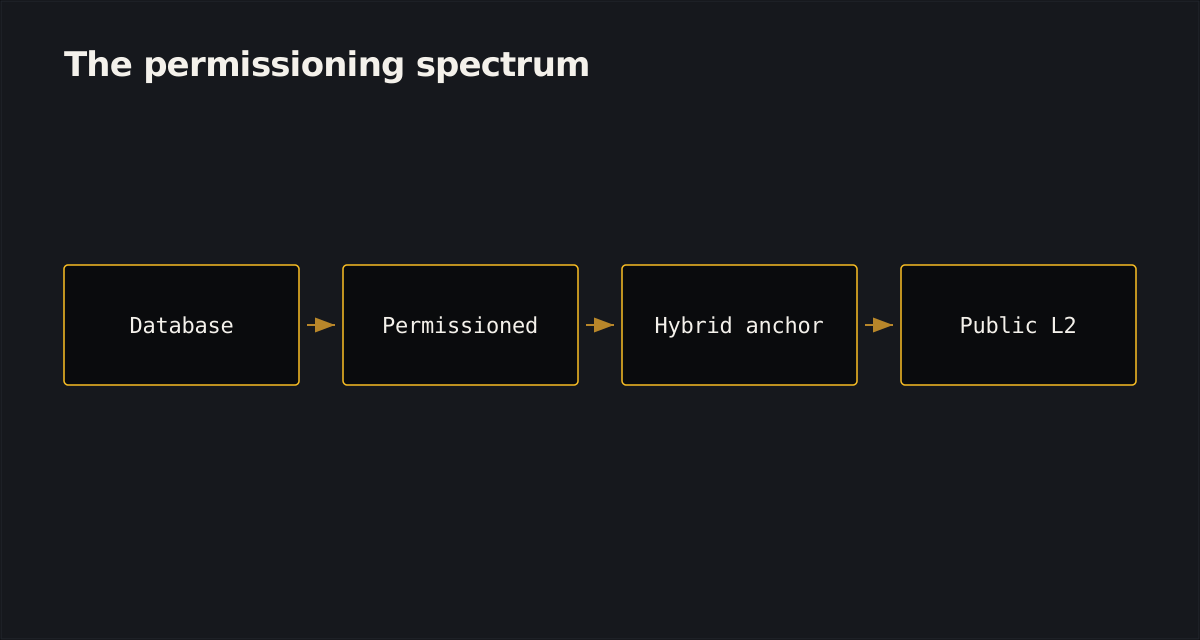
A permissioned chain controls who can join. Identities are known, there's typically no public token, and sensitive data stays visible only to the parties that need it, the natural fit for a bank consortium or a supply-chain network. A public chain like Ethereum or Polygon is open by design: anyone can transact, validators are pseudonymous, and no single party controls it, exactly the property you want when an asset must be publicly tradable or when no group member should be able to shut the ledger down.
The hybrid model is where most of the interesting 2026 activity sits. KfW and DZ BANK didn't run a private copy of a ledger for their March 2026 bond; they issued and settled directly on public Polygon infrastructure, with Germany's Bundesbank supplying the settlement layer and enterprise controls (allowlists, registry functions through Cashlink, ISIN assignment through WM Datenservice) doing the permissioning work that used to require a separate network. That's the same pattern as asset tokenisation generally: keep the proof on a chain anyone can independently check, keep the sensitive data off it.
Default to permissioned or hybrid. Reach for a fully public deployment only once you can name the specific party you don't want controlling the ledger.
Enterprise blockchain platforms and tools compared
There's no single best enterprise blockchain platform. The right one follows the trust and privacy model your use case needs.
A few notes the table can't carry. Hyperledger Fabric and Besu both moved under LF Decentralized Trust when the Linux Foundation folded Hyperledger Foundation into the new umbrella in September 2024, and both stay Apache 2.0 licensed. Fabric's private channels keep sensitive data need-to-know, still why it's the default for supply-chain consortia. Besu absorbed ConsenSys's Quorum lineage after GoQuorum was sunset in 2023, so it's now the reference client for both public Ethereum work and permissioned deployments, a path our own web3 development work draws on when a client already knows Ethereum tooling.
R3 Corda ships as Apache 2.0 with a commercial enterprise edition; its privacy model is point-to-point rather than broadcast, a transaction is shared only with the parties to it and the notary confirming it hasn't been double-spent. R3 trimmed its Irish headcount through 2024 and 2025 but remains independently owned. Digital Asset's Canton runs on Daml, which builds privacy into the contract model itself (signatories, observers, and controllers define who can see what), splitting every transaction into views so a validator only sees the parts naming its own parties.
Polygon and the XRP Ledger represent the public-with-enterprise-controls pattern above: Polygon's own institutional page lists Stripe, Mastercard, and Securitize as integration partners, and Ripple's RLUSD stablecoin, launched 17 December 2024 under a New York trust charter, backed 1:1 by cash and short-term Treasuries, is now wired into Ripple's institutional payments product. RLUSD is a fiat-backed stablecoin, the same category our guide to DeFi protocols covers, settling on the same public rails. Hedera sits apart structurally, governed by a council of more than 30 organizations, including Google, IBM, FedEx, and Deutsche Telekom, each with equal voting rights and a term limit so no single member controls the network. Whatever you pick, the code carries the actual business logic and needs the same audit-first discipline regardless of which chain sits underneath.
How enterprises adopt blockchain without a dead-end pilot
The reason so many enterprise blockchain efforts end as a slide deck about a successful pilot is that the pilot proved the technology runs while never proving anyone needed it. Avoiding that is mostly about sequencing, and TradeLens and we.trade both failed the same sequencing test. Fair warning: the fix below is less about engineering than most teams expect, and the political part is the part nobody wants to own.
What an enterprise blockchain proof of concept platform actually needs
A proof of concept platform needs three things a sandbox demo doesn't: named participants with a real reason to be there, the privacy and permissioning controls the production system will need, and an integration path into a real system of record. Synthetic data and a single internal user prove the code executes and nothing else, which is most of what went wrong with the wave of 2018 to 2021 pilots.
- Start with the problem, not the chain. Write down the multi-party reconciliation pain being solved and who else has to participate. Can't name the other organizations and what they gain? Stop. It's a database project wearing a costume.
- Line up the consortium before you build. A shared ledger with one participant is a contradiction. Get the other parties to commit to governance and real data, early, exactly the step we.trade never cleared.
- Pick the platform last, and pick it for fit. Once the problem and participants are real, privacy and performance needs point clearly at permissioned, public, or hybrid.
- One workflow, real participants, real data, that's the whole scope of a good thin slice. Audit it like it holds money regardless: the same failure modes that drain public protocols apply here too.
The table below is a modelled timeline, not a quote: typical project shapes, including our own Chaindoc build. Consortium alignment carries the widest range, since it depends on how many outside organizations must agree, not on how fast any one team can build.
Compliance follows the type of asset, not the technology. In the EU, a tokenised bond or share that qualifies as a financial instrument stays under MiFID II and the Prospectus Regulation, not MiCA: Article 2(4) of the MiCA regulation excludes crypto-assets that already qualify as financial instruments. The infrastructure that trades or settles those instruments can instead run under the DLT Pilot Regime, in force since 23 March 2023, which caps individual bond issuances under EUR 1 billion while the market tests the model. MiCA itself governs what sits outside existing financial law: stablecoins and other crypto-assets that aren't already securities or deposits.
Data protection is a separate, older tension that tokenisation doesn't remove. The European Parliament's 2019 study on blockchain and the GDPR found the regulation assumes a single controller for each piece of personal data, and that data can be modified or erased on request, both of which sit uneasily against a ledger designed to resist that kind of change. Every serious deployment we've seen resolves this the way our own builds do: personal data stays off-chain, only a hash goes on the ledger, so the chain proves integrity without holding anything a regulator could ask you to erase. Whether to build on a shared platform or run something purpose-built is the same build-versus-buy question we walk clients through first.
Real proof from inside Idealogic's own builds
We've built on both sides of the blockchain-or-database line in enterprise work, and the contrast between our own projects is the most honest evidence we can offer.
When we built HaulBreeze, our own supply-chain management product, we put inventory, orders, and compliance documents on one unified data layer, not a distributed ledger. Idealogic is the sole owner of that system, so there was no multi-party trust problem to solve, and a chain would have added latency for a guarantee nobody needed. That decision is itself a live example of the rule from earlier in this guide: when one company owns the data, build the database.
Where the multi-party condition is real, we've built the chain instead. Chaindoc is an eIDAS- and ESIGN-qualified e-signature platform we built across four regulated sectors: real estate, healthcare, insurance, and IT services. Every signature writes a SHA-256 hash of the signed document to an on-chain audit trail, so anyone can later re-hash the file and prove it hasn't changed since signing, without taking Chaindoc's own database on trust. The documents stay off-chain, only the hash goes on the ledger. Per the case study, Chaindoc has processed over 10,000 signed documents across more than 500 active client teams at 99.9% uptime.
e-States is our tokenisation case: a platform that splits commercial real estate into on-chain tokens, so a building that used to need a seven-figure check now supports fractional ownership through a crowdfunding raise. Token contracts hold ownership on-chain, while property records stay off-chain, with the chain holding only the anchor tying the two together. It's the same hybrid split KfW's bond and HSBC's Orion both lean on.
Where this leaves you
Enterprise blockchain in 2026 is neither the transformation the 2018 marketing promised nor the dead end the failed pilots suggest. It's a narrow, well-proven tool: when several organizations must agree on one record and no single one of them should own it, a permissioned ledger, or increasingly a public chain with enterprise controls layered on top, does something a database genuinely can't. Outside that band, the honest answer is still to build the database.
The technology risk in enterprise blockchain has mostly gone away. Fabric, Corda, Canton, and the public L2s are mature enough to trust with real institutional money, and the platforms processing trillions of dollars a year prove it. What decides an outcome now is whether the other organizations actually show up: whether the consortium forms, whether the integration reaches a real system of record, and whether the pilot was scoped to prove something rather than to dodge the hard parts.
That's the conversation our blockchain development team has with every client before a line of code gets written: is there a real multi-party problem here, and which trust model fits it. If the answer points at a chain, we build it permissioned-first and audit-first. If it points at a database, we'll tell you that too, the way we told ourselves when we built HaulBreeze.
CTO and Co-founder at Idealogic. Directing engineering, systems architecture, security, and full-stack delivery across web, mobile, and blockchain.
Frequently asked questions
Enterprise blockchain is a permissioned, shared ledger a known group of organizations use to agree on one set of records, instead of each side keeping its own copy and reconciling by hand. Only vetted, identified participants can read or write. In 2026 the term also covers a newer pattern: a bank transacting directly on a public chain, such as Polygon, with permissioning enforced at the application layer instead of a private network.
JPMorgan's Kinexys platform (renamed from Onyx in November 2024) had processed over $4 trillion in transaction volume since inception and was running about $7 billion a day by September 2026, according to JPMorgan's own newsroom. Broadridge's Distributed Ledger Repo platform processed $357 billion a day in average repo volume in June 2026. HSBC's Orion platform has issued more than $3.5 billion in digitally native bonds and was awarded the mandate to build the UK's pilot for a tokenised sovereign bond. These are production systems moving real institutional money, not pilots.
No, but the pilot-heavy phase is over, and the survivors look different from what got hyped around 2018. Maersk and IBM discontinued TradeLens in November 2022, and the 12-bank we.trade consortium became insolvent in mid-2022, both because too few independent organizations ever committed real data to the shared ledger. At the same time, JPMorgan's Kinexys platform has processed over $4 trillion since inception, and Broadridge's repo platform moves hundreds of billions of dollars a day. What died was the version of enterprise blockchain that needed a voluntary consortium of competitors to show up. What survived is owned and operated by a single institution large enough to drive adoption across its own network.
A public blockchain like Ethereum is open: anyone can transact, validators are pseudonymous, and no single party controls it. An enterprise blockchain is permissioned: membership is controlled by legal agreement, every participant has a known identity, and there is usually no public token or gas fee. The two aren't always separate networks anymore. A growing share of enterprise activity, including KfW and DZ BANK's March 2026 digital bond, which settled in about an hour instead of the usual five days, runs directly on a public chain like Polygon, with the enterprise controls (allowlists, transfer restrictions, role checks) enforced at the application layer instead of the network layer.
The platforms enterprises evaluate most are Hyperledger Fabric and Hyperledger Besu, both governed by LF Decentralized Trust since September 2024, R3 Corda, Digital Asset's Canton Network built on the Daml language, public EVM networks such as Polygon or Ethereum for enterprise use, the XRP Ledger, and Hedera, governed by a council of more than 30 organizations including Google, IBM, and Deutsche Telekom. There is no single best answer. Fabric and Corda suit private consortia, Canton and Daml suit institutions that need contract-level privacy without running a fully separate network, and Polygon or the XRP Ledger suit a bank that wants to settle on public, always-on infrastructure.
A real problem with named participants, not a sandbox demo. It needs the same privacy and permissioning controls the production system will need, plus an integration path into a real system of record, and, for tokenised financial instruments in the EU, a route through the DLT Pilot Regime. Most failed pilots proved the technology worked and nothing else, because they avoided the hard parts: consortium governance and live integration.
There's no fixed number, because consortium governance is usually the slowest and least predictable phase, not the engineering. As a worked example, our own Chaindoc build, which anchors every signature to an on-chain hash for four regulated sectors, ran discovery and compliance mapping for three weeks, signing-flow and access-model design for seven weeks, engineering for eight weeks, and audit prep for four weeks: 22 weeks end to end with one squad. A true multi-party pilot typically adds several more weeks up front for consortium and governance alignment, because that step depends on how many outside organizations have to agree, not on how fast your own team can build.
Most fail because they start with the technology and reverse-engineer a use case to justify it, or because the consortium never actually forms. TradeLens proved the technology could track shipping containers and still shut down in 2023 because Maersk and IBM said the platform had not reached commercial viability and full industry collaboration was never achieved. we.trade folded the same year for a related reason: the participating banks could not agree on further investment. The pattern holds across both failures: a pilot can prove the tech runs and still fail, if the other organizations it needs never fully commit.
More from the journal

Banking Software Development: Systems, Regulation, and Cost
Banking software development is the engineering of the systems a bank runs on: the ledger, the channels, the payment rails, and the compliance layer around them. What each layer does, which rules bind it, how to integrate a legacy core, where crypto fits, and what a build costs.

What Is Fintech and How It Is Changing the Way We Handle Money
Fintech, short for financial technology, is software that delivers financial services without the old bank branch in the middle. This guide covers what fintech is, its main types, how it works under the hood, and how it is changing the way we handle money.

How to Read a Cryptocurrency Market Forecast in 2026
A cryptocurrency market forecast is a set of scenarios, not a prediction you can bank on. This guide explains the forces that move the crypto market, from halving cycles and interest rates to ETFs, regulation, and stablecoins, and how to read any outlook without gambling.