Smart Contract Development: Lifecycle, Patterns, Cost
Smart contract development is mostly verification, not typing. This guide walks the lifecycle from specification to monitoring, with Solidity code, a language and chain comparison, exploit losses measured from DeFiLlama, and what an audited build costs.

Smart contract development is the work of specifying, writing, testing, auditing, deploying and operating programs that run on a blockchain and enforce rules without an operator who can override them. Ethereum's own documentation describes a smart contract as a program that lives at a specific address and carries its own code and state. That address is public, the bytecode is usually frozen, and interactions with it are irreversible. Everything unusual about this discipline follows from those three facts.
This guide is written from the build side. It walks the lifecycle stage by stage, names the tools teams actually run in 2026 with their current versions, shows the DeFi patterns you will end up writing, and puts numbers on the two questions clients ask first: what it costs and how long it takes.
The short version
- The lifecycle runs specification, architecture, implementation, testing, audit, deployment and monitoring. Writing code is the smallest stage in it.
- Solidity is the default because the EVM bytecode it produces runs unchanged on Ethereum, Base, Arbitrum, Optimism and Polygon. Rust plus Anchor covers Solana, Move covers Aptos and Sui.
- Of the $9.25 billion DeFiLlama records lost across 920 attacks on DeFi protocols, the largest single category is a compromised key at $1.92 billion, ahead of every code bug class.
- Access control errors cost $1.54 billion and share accounting errors $1.36 billion, which is more than oracle manipulation and re-entrancy put together.
- An audited build costs two lines: engineering, and the audit itself. Sherlock's 2026 reference puts a mid-complexity DeFi audit at $40,000 to $100,000.
- Deployment gas is now rounding error. A contract at the 24,576-byte ceiling cost about $1.22 to deploy on Ethereum mainnet on 10 September 2026.
What smart contract development is
A smart contract is a program with a bank account. It holds state, it holds assets, and it applies rules that the network enforces rather than a company. Ethereum's docs reach for a vending machine as the analogy: money plus a selection equals a snack, with nobody in the middle deciding whether you deserve one. What makes the analogy useful is that the machine's behavior gets fixed before anyone puts a coin in.
Smart contract development is therefore an odd kind of software work. Deployed code cannot be deleted by default and, in most designs, is immutable once it lands. There is no staging window between a bug shipping and an adversary finding it, because the adversary reads your source on the block explorer at the same moment your users do. The whole discipline is arranged around that asymmetry.
What a smart contract developer does
A smart contract developer designs the on-chain half of a product and then spends most of the week trying to break it. The job starts with a business rule and ends with a state machine: which states the contract can occupy, which transitions are legal, who may trigger each one, and what must remain true regardless of input. From there it is Solidity, Rust or Move, then unit tests, then fuzzing and invariant runs, then static analysis, then fixing what an external audit finds, then a deployment script that gets dry-run on a testnet before it touches mainnet, then source verification, then monitoring the live address. Somewhere in that list is the part where you type the contract, and it is not the part that takes the time. A good developer also knows which parts of the product should never go on chain at all.
What an example of a smart contract looks like
Escrow is the cleanest example, because the contract's job is exactly the job a person used to do. Funds sit in the contract instead of with an agent, the contract carries the conditions both parties agreed to, and it releases to the seller or refunds the buyer when those conditions resolve. We built that for Zert, a smart contract escrow platform where escrow accounts hold the value and contract code referees the exchange, with the whole thing hidden behind ordinary product screens.
The other everyday example is a token. An ERC-20 contract tracks balances, moves them on transfer, and lets one address spend on another's behalf through an allowance. On top of a standard library that is about a hundred lines, which is why token work is the entry point for most teams and why creating a cryptocurrency is a solved problem compared with everything downstream of it.
The smart contract development lifecycle, stage by stage
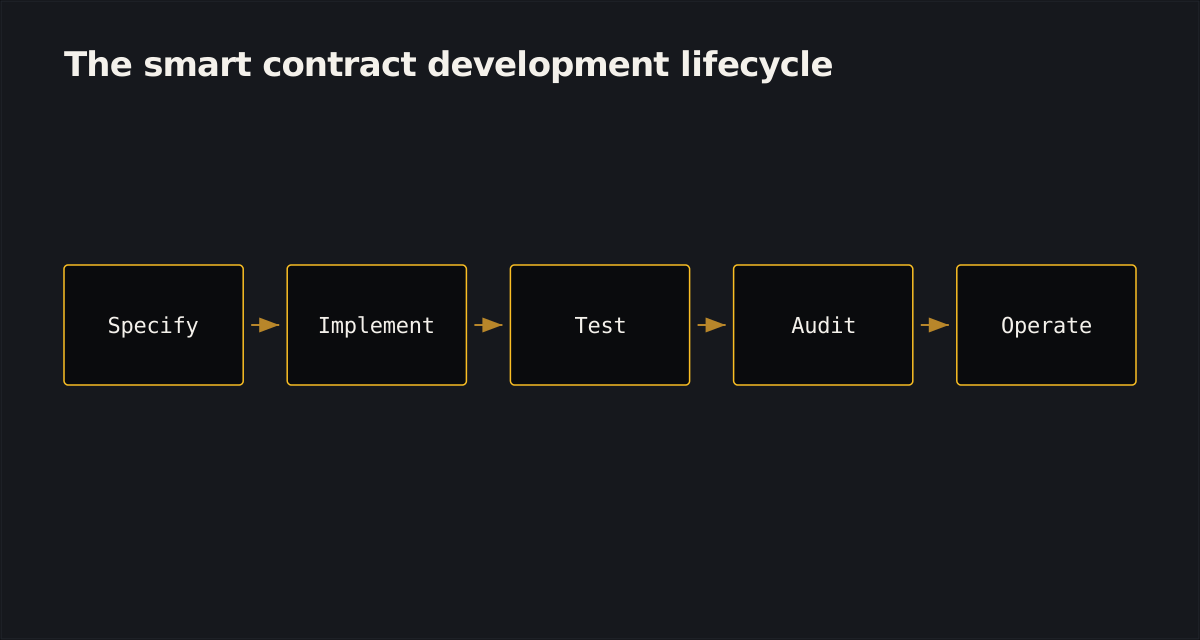
Every stage below settles a specific decision. Skipping a stage does not remove the decision, it just moves it somewhere it costs more to reverse. OpenZeppelin's own readiness guide organizes the same ground into plan, code, test, audit, deploy and monitor, which is a useful cross-check that this is the industry's shape and not one agency's house style.
Smart contract development starts with a spec
The decision it settles: what must always be true. Before any code, write the state machine and the invariants. The sum of all shares equals total supply. Recorded assets never exceed the contract's actual balance. No account can withdraw more than it deposited plus what it earned. These sentences become your fuzzing oracle later, which is why vague ones produce vague tests.
The threat model is the other half. What happens if the same function is called twice in one block? If a token transfer returns false instead of reverting? If the oracle returns zero, or a stale price, or a price that moved 40 percent in one block? Write the answers down while changing them is free.
Architecture and contract patterns
Architecture is where you decide how much surface you are exposing. You choose how many contracts there are, which of them hold funds, whether anything is upgradeable, and what stays off chain entirely. That last question is the one most teams underweight. On SeedBox, the DeFi investment platform we built for a crypto venture group, the split was deliberate: trustless logic and settlement went into Solidity, while investor profiles, verification status, tier assignments and referral graphs stayed in PostgreSQL where they are fast and fixable. A smaller contract surface is a smaller audit and a smaller blast radius.
Upgradeability is a real trade. A proxy lets you fix a bug; it also hands anyone who takes your admin key the ability to replace the entire contract. DeFiLlama records $166 million lost across seven incidents to uninitialized proxies alone, including the $150 million Parity multisig freeze in November 2017.
Implementation: Solidity development in practice
Good Solidity is deliberately boring, and the decision this stage settles is how much of it you write yourself. Standard tokens, access control, pausing and re-entrancy guards come from OpenZeppelin Contracts, on v5.7.0 since 29 July 2026, so the only novel code in the repository is the protocol's actual logic. The compiler moves faster than people expect: Solidity 0.8.37 is the current release as of 10 September 2026, and the 0.8 line has made arithmetic overflow revert by default since 0.8.0 in December 2020.
Two habits matter more than any style guide. Order every function as checks, then effects, then interactions. And treat every external address as hostile, because a token you call might be a contract written to call you back mid-execution.
Testing: unit, fuzzing and invariants
The decision it settles: whether your invariants survive input you did not imagine. Unit tests are the floor. The layer that finds real bugs is property-based: a fuzzer throws thousands of randomized call sequences at the contract and checks that the invariants from stage one still hold.
The current toolchain is short. Foundry v1.8.1 ships forge, cast, anvil and chisel, with fuzzing and invariant testing built in and documented handler-and-ghost-variable patterns for stateful runs. Hardhat 3 went stable on 1 June 2026 and now runs Solidity tests alongside TypeScript ones, on 3.16.0 as of 7 September 2026. For deeper campaigns, Trail of Bits maintains Echidna v2.3.3 and its Go-based sibling Medusa v1.5.1, and Certora ships a formal-verification prover, on 8.19.2 as of 7 September 2026. Fork testing against live mainnet state is not optional either, because that is where you meet the fee-on-transfer token that breaks your accounting.
Ethereum's testing documentation is candid about the ceiling here: rigorous testing rarely guarantees the absence of bugs. Which is the argument for the next stage.
Audit
The decision it settles: whether anyone who did not write the code agrees it is safe. Run Slither first, on 0.11.6 since 28 July 2026 with about a hundred detectors, so the automated bug-class signatures are gone before a human bills you for finding them. Then commission an external review.
What separates a useful audit from a logo on a PDF is whether the auditors run their own tooling and write their own tests rather than skimming yours, and whether findings arrive with a reproducible proof-of-concept rather than a paragraph of concern. Severity grading has to be honest too, which is easier to check than it sounds: ask what the last three criticals were. Plan for findings, a rewrite and a second round after the fixes, because a first-pass clean report usually means the scope was too narrow. Our full smart contract audit walkthrough covers what a report should contain and how to read one.
Deployment: testnet, mainnet, verification
Deployment is code: reviewed, dry-run on a testnet, never typed into a console. The decision it settles is who holds power over the live contract afterwards. Constructor arguments, initial owners and admin roles get checked twice, because a mistyped owner address is unrecoverable. OpenZeppelin's guide makes a specific point of not assigning roles from msg.sender in a deploy script, which is how deployer keys end up as permanent admins by accident.
After deployment, verify the source on the block explorer. An unverified contract asking for token approvals is a signal informed users read correctly.
Monitoring and upgrades
The decision this last stage settles is how fast you find out. A live contract is production, and production needs observability: event streams, treasury balances, alerts on abnormal flows, and an incident runbook that names who can pause what.
This is also where the tooling shifted recently, and it is worth knowing before you build a runbook around a product that is gone. OpenZeppelin Defender closed new sign-ups on 30 June 2025 and shut down on 1 July 2026, with its Relayer and Monitor functions moved to open-source projects that OpenZeppelin still ships and updates. Tenderly remains the other common choice, with transaction simulation, an opcode-level debugger, gas profiling and alert routing.
Smart contract languages and chains, compared
Solidity is the default, and the reason is bytecode portability rather than language design. The same compiled artifact runs on Ethereum and on every EVM-compatible chain, so a team that learns one execution model can ship to several networks. Ethereum's languages documentation names Solidity and Vyper as the two most actively maintained options for the EVM, with Yul as a low-level intermediate language and Fe still early.
Vyper is the deliberate minimalist: Python-shaped, no inheritance, no modifiers, no inline assembly, on purpose, so a reviewer has less to hold in their head. Curve's stableswap contracts are the best-known production codebase written in it.
Off the EVM the model changes more than the syntax. Solana programs are stateless and account-based, and Anchor hides most of the account-validation boilerplate, on 1.2.0 since 4 September 2026. Move takes a different route again: Sui's version removes global storage entirely so transactions on unrelated objects can execute in parallel, and every object carries an id field of type UID as its first property. Aptos runs a Move 2 compiler with a formal-verification prover in the standard toolchain.
The practical read: pick Solidity unless a specific chain requirement pushes you off it, because the auditor pool, the library ecosystem and the volume of public post-mortems are all deepest there. The wider architectural context of that choice sits in our guide to web3 development.
DeFi contract patterns you will actually write
Most DeFi products are recombinations of four patterns, and smart contract development in DeFi is mostly a matter of knowing which one you are in. Learning them properly is what lets you notice when something is subtly wrong, and each one has a signature failure mode with a measured price tag attached. The categories those patterns serve are mapped in our explainer on DeFi protocols and their types.
Vaults and share accounting
A vault takes deposits, does something productive with them, and tracks each depositor's claim as shares. ERC-4626, created in December 2021 and now final, standardized the interface so vaults compose predictably, and it is explicit that rounding should favor the vault over its users.
The skeleton is short, because the standard library carries the accounting. Everything below compiles with Solidity 0.8.37 against OpenZeppelin Contracts v5.7.0, whose ERC4626 extension requires pragma solidity ^0.8.24.
That override is the whole point of the example. The classic vault bug is the inflation or donation attack: someone deposits one wei, receives one share, then sends a large amount of the underlying token straight to the vault. One share is now worth a fortune, and the next honest deposit rounds down to zero shares. OpenZeppelin's ERC-4626 documentation works through the arithmetic and shows that virtual shares plus a decimals offset flip the economics, so the attacker loses at least as much as the victim deposits.
This is not a museum piece. DeFiLlama attributes $373 million across fifteen incidents to donation attacks, including Euler V1 at $197 million in March 2023 and Tectonic at $124 million on 30 August 2026.
Automated market makers
An AMM replaces the order book with a formula. The constant-product model holds x * y = k across two reserves, so price slides along a curve as people trade against the pool. No counterparties, no bids, just an equation and some liquidity.
The subtleties live at the edges. Every swap needs a minimum-output check and a deadline, or a bot sandwiches the trade and takes the difference. Pools that assume the amount received equals the amount sent break on fee-on-transfer and rebasing tokens. And the pool's spot price is manipulable inside a single transaction, which makes reading it as an oracle one of the most expensive habits in the space. We go deeper into the mechanics and the operator economics in our guide to decentralized exchange development.
Staking and reward distribution
Staking pays out over time in proportion to stake. The naive version loops over stakers to update balances and runs out of gas the moment the protocol succeeds. The standard fix is an accumulator: track one global reward-per-token figure, store each account's value at its last interaction, and compute pending rewards as the balance multiplied by the difference. Constant gas, no loops, correct for everyone.
The failure mode is ordering. Update the accumulator after a balance change instead of before and rewards leak, quietly, on every deposit and withdrawal path you forgot to touch. If the token itself has emission rules that interact with this, our guide to tokenomics covers the design side of that question.
Lending, and the re-entrancy pair everyone should be able to write from memory
Lending markets combine the other three: collateral in a vault, prices from an oracle, interest accruing per block. They are also where the oldest bug in the field still lands. Here is the version that gets drained.
The recipient is a contract. Receiving funds hands it control, it calls back into withdraw while balances still says it is owed money, and it repeats until the pool is empty. The fix is two changes, used together.
Modern tokens make the trap easier to fall into. ERC-777 and several NFT standards call the recipient on every transfer, so a function can be re-entered through what looks like a plain token movement.
The patterns in DeFi are public knowledge. The exploits succeed on the seams between them, in the integration nobody audited because each piece looked fine alone.
Smart contract security pitfalls, measured by what they cost
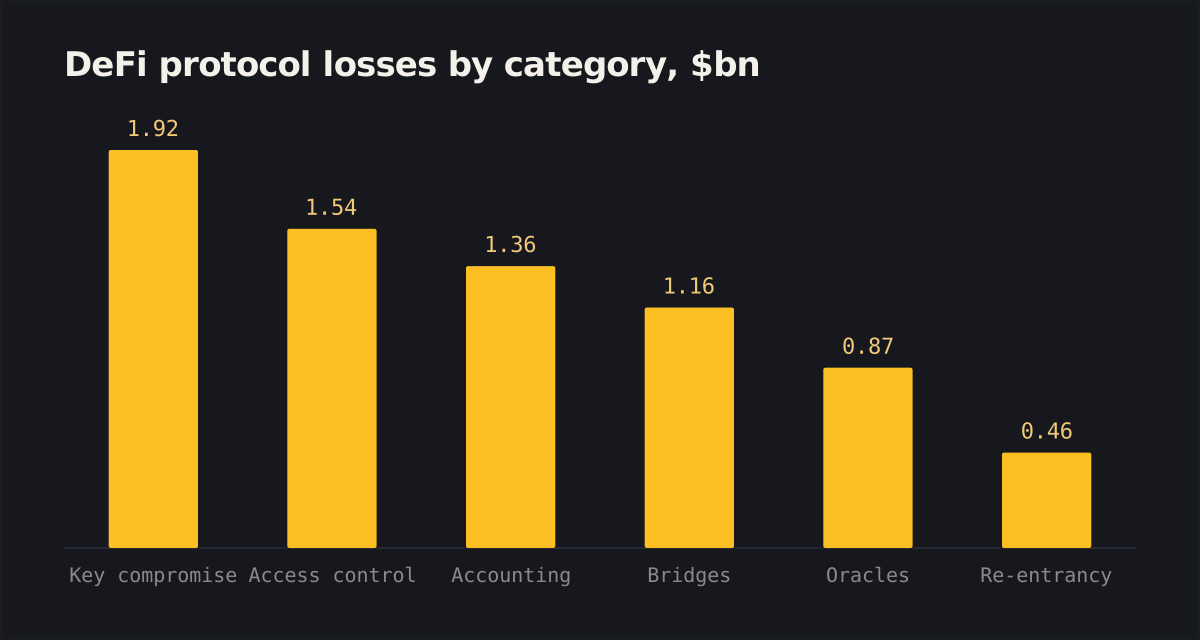
DeFiLlama's hack database records $9.25 billion lost across 920 attacks on DeFi protocols, out of $20.65 billion across 1,263 incidents when you count exchanges, bridges, tokens and everything else. Sorted by DeFiLlama's own categories, the biggest line is not a Solidity bug at all. Key compromise accounts for $1.92 billion across 68 incidents, ahead of access control at $1.54 billion, share accounting at $1.36 billion, bridge and cross-chain flaws at $1.16 billion, oracle manipulation at $874 million and re-entrancy at $455 million.
Chainalysis reads the same trend from the other direction. Its 2026 report on stolen funds, published 18 December 2025, puts total crypto theft above $3.4 billion for 2025, with centralized services taking 88 percent of losses in the first quarter and the single Bybit compromise accounting for $1.5 billion. It also notes that DeFi hack losses stayed suppressed through 2024 and 2025 even as value locked in DeFi grew.
Both readings point the same way. Contract bugs are getting caught more often than they used to. The keys are not.
A few details in that data are worth carrying around. Validator key compromise is the single most expensive technique at $888 million across seven incidents; improper access control is the costliest bug class at $878 million across 104 incidents, ahead of spot price manipulation at $815 million. Arithmetic and rounding errors still cost $500 million and $199 million respectively even after Solidity 0.8 made overflow revert, because truncating division is not overflow. And 2026 is not a quiet year: 183 attacks on DeFi protocols through 9 September, worth $1.15 billion.
The broader operational picture, including key custody and the parts of the stack that are not contracts at all, sits in our guide to blockchain security.
How much smart contract development costs, and how long it takes
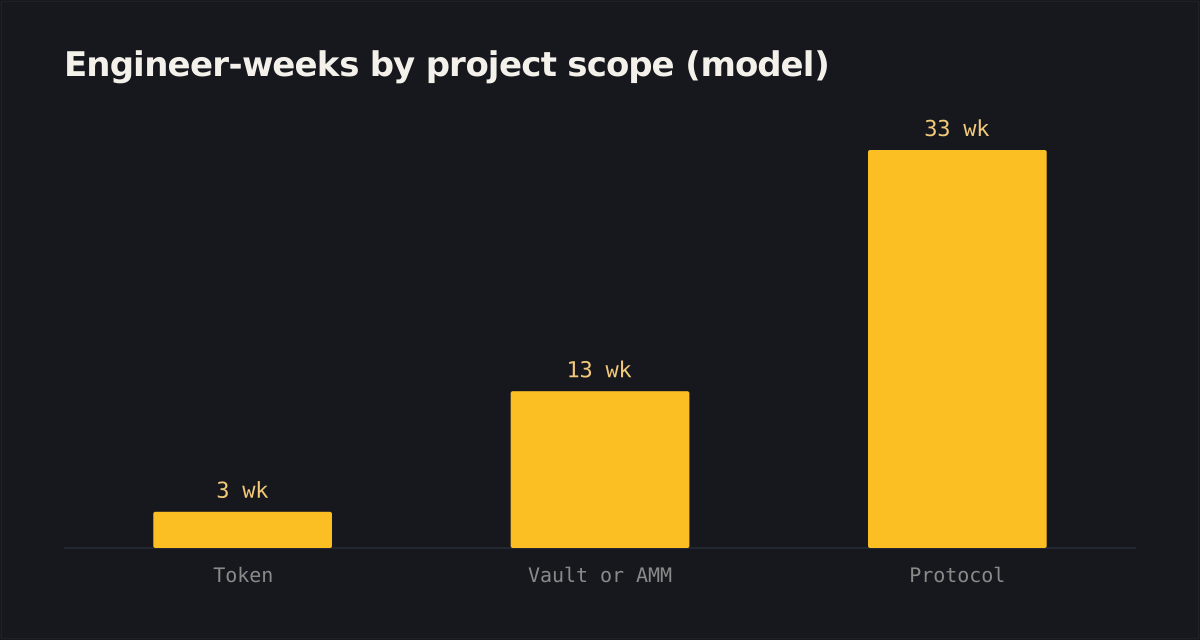
Two lines dominate the budget: your engineering, and somebody else's review. The table models the first and quotes published figures for the second. Assumptions, so you can substitute your own: an engineer-week is priced at $4,800, which is forty hours at a $120 blended rate; the scope includes tests, fuzzing harness and deploy scripts, not the front end, indexer or backend around the contract.
The audit column comes from Sherlock's 2026 pricing reference, published 18 February 2026, which puts the market at $5,000 to $250,000 and above, breaks it into those three tiers, and adds $5,000 to $20,000 per remediation pass. Its own budgeting advice for a mid-complexity DeFi protocol before launch is $60,000 to $120,000 including at least one remediation review, which is the number worth showing a board.
Competitive audits price differently. Code4rena's sponsor documentation says the cost is simply the award pool the sponsor chooses, with no platform fee, so the lever is how much attention you want to buy rather than a rate card.
Notice what the calendar column is really measuring. Contract implementation on a vault is a few weeks; the months come from the audit queue, the remediation round and the second look afterwards. Book the audit slot when you write the spec, not when the code is finished.
What deploying actually costs on chain
Gas is the line clients expect to be large and is not. Putting code on Ethereum costs 200 gas per byte of deployed bytecode, plus 32,000 for the CREATE itself and the 21,000 base cost of the transaction, per the Ethereum execution specs. A contract at the 24,576-byte ceiling that EIP-170 sets therefore costs roughly 4.97 million gas to deploy.
Ethereum's base fee was 0.10 gwei at block 25,946,617 on 10 September 2026, and ether traded at $2,460 that day. That prices the largest contract the protocol will accept at about $1.22 to deploy. Constructor execution adds to it, gas prices move, and an L2 costs less again, but the order of magnitude is the point: deployment is not a budget line, the review is.
How to become a smart contract developer
Smart contract development hires for two things: knowing the execution model, and knowing how to attack it. In practice that means Solidity and the EVM first, since gas, storage layout and the call model explain most of what looks arbitrary in the language, then the testing stack, because that is what employers are short of.
Ethereum's learning tools page is the least commercial starting list: Remix for writing contracts in the browser with nothing installed, SpeedrunEthereum for challenge-driven building, and Cyfrin Updraft, which it describes as a free hands-on curriculum for Solidity, security, Foundry and DeFi.
After the tutorials, the fastest progression is unglamorous. Read published audit reports end to end, then rebuild two or three of the findings as failing Foundry tests until the exploit runs locally. The second habit is writing invariants for a protocol you did not build and fuzzing them, which teaches you to read somebody else's code the way an attacker does. Then enter a public competitive audit, where the work is graded by whether you found something real. Somebody who can explain why a rounding direction favors the protocol and prove it with a test is more employable than somebody who has shipped five tokens.
Choosing a smart contract development company
If you are buying rather than building, the useful questions are about practice, not portfolio. Ask to see the test suite, specifically the fuzzing and invariant tests rather than unit coverage. Then walk through a past audit with them: what was found, at what severity, and how it was fixed. A team that has never had a serious finding has either been lucky or has not shipped much. Key custody is the next question, and the answer should involve multisigs and timelocks rather than a lead developer's wallet. Finish with the one nobody rehearses: what happens at three in the morning when the alerts fire.
Then ask about everything that is not a contract. Most on-chain products need a front end, an indexer, off-chain signing and a conventional backend, which is the subject of our guide to building a dApp. A vendor who only talks about Solidity leaves you integrating the hard parts. For a wider survey of the market, our list of blockchain development companies sets out how the field is structured, and our DeFi development company guide covers vendor selection for decentralized finance specifically.
What we can show on our side is a mixed record, which is the honest kind. SeedBox is a crypto venture-investing platform built from the idea stage, with the product requirement document written before the first line of Solidity, contracts written in Solidity with Ethers.js and Web3.js, and the on-chain and off-chain split described above. Zert is an escrow platform where the contract is the referee, with web, mobile and contracts delivered by one squad. Glue is a gold-backed trading platform where we worked the centralized, decentralized and hybrid trade-off in discovery instead of picking a label up front.
And Planetcoin, a crypto exchange platform built around a first-time buyer paying by card, has no smart contracts in it at all. That is not a gap in the case study. Shared, verifiable state is a requirement some products have and others do not, and a partner who cannot tell you which one you are is not saving you money. For the market context behind that judgment, our piece on DeFi as a trend is the wider view.
What smart contract development actually demands
Smart contract development rewards teams that treat verification as the deliverable and the code as an intermediate artifact. The patterns are public, the bug classes are documented, the tooling to catch them is mature and mostly free, and the measured loss data says the surviving weak point is increasingly operational rather than syntactic: keys, roles, upgrade paths and who can sign what at three in the morning.
Nothing in the lifecycle above is exotic. Specify the invariants, keep the contract surface small, build on libraries that have already been attacked, fuzz the properties you wrote down, get a review from people who did not write the code and are not attached to your launch date, and deploy behind a timelock with a pause switch and caps you raise as confidence grows. That is what our blockchain development team does on every engagement, and the reason to meet that bar before the contract is live is that afterwards, the option is gone.
Frequently asked questions
It is the work of specifying, writing, testing, auditing, deploying and operating programs that run on a blockchain and enforce rules nobody can quietly override. Because deployed bytecode is public and usually cannot be patched after launch, most of the effort in smart contract development goes into verification rather than into writing code, which is the opposite balance to ordinary backend work.
A smart contract developer designs the on-chain half of a product and then tries to break it. The week looks like this: turn a business rule into a state machine and a list of invariants, write the contract in Solidity, Rust or Move, cover it with unit tests, fuzzing and invariant runs, feed it to static analyzers, fix what an external audit finds, script the deployment, verify the source on the block explorer, and watch the live contract afterwards. Coding is the smallest slice.
Budget in two lines: engineering and audit. A single-purpose contract such as a token runs two to four engineer-weeks, a DeFi vault or AMM runs ten to sixteen, and a protocol with governance and upgrades runs twenty-six or more. On the audit side, Sherlock's February 2026 pricing reference puts a simple token at $5,000 to $20,000, a mid-complexity DeFi protocol at $40,000 to $100,000, and enterprise multi-chain systems at $150,000 and up, with each remediation pass adding $5,000 to $20,000 on top. Its own pre-launch guidance for a mid-complexity protocol is $60,000 to $120,000 including one remediation review. Deployment gas barely registers next to either line, so leave it out of the estimate.
Learn Solidity and the EVM execution model first, then learn to attack what you wrote. Ethereum's own learning-tools page points at Remix, SpeedrunEthereum and Cyfrin Updraft, which covers Solidity, security, Foundry and DeFi for free. After that, read published audit reports line by line, rebuild the exploits in a local Foundry test, and join a public competitive audit. Employers hire for the second half of that list, because writing a contract that compiles is not the scarce skill.
An escrow is the clearest one. Funds sit in a contract instead of with a middleman, the contract holds the conditions both sides agreed to, and it releases to the seller or refunds the buyer when those conditions resolve. Idealogic built exactly that for Zert, where escrow accounts hold the value and contract code settles the trade. A token contract is the other everyday example: ERC-20 balances, transfers and approvals, roughly a hundred lines on top of a standard library.
A token or single-purpose contract takes two to four engineer-weeks and about a month of calendar time. A DeFi vault or AMM takes ten to sixteen engineer-weeks, and roughly three to four months once you allow for the audit queue and a remediation round. A protocol with governance, upgrade paths and several interacting contracts takes twenty-six weeks or more of engineering and six to nine months of calendar time. Audit scheduling, not typing, is what usually sets the launch date.
Solidity, for most projects. It targets the Ethereum Virtual Machine, so one compiled artifact runs on Ethereum, Base, Arbitrum, Optimism and Polygon, and it carries the deepest tooling, library and auditor pool of any option. Vyper is the smaller, deliberately minimal EVM alternative. Off the EVM, Solana programs use Rust with the Anchor framework, and Aptos and Sui use Move.
Any contract that will custody value does. Deployed bytecode is public and usually immutable, so an attacker can study it at leisure while you cannot patch it. Ethereum's testing documentation is blunt that rigorous testing rarely guarantees the absence of bugs, and names audits and bug bounties as the ways to get other people analyzing your code. One external audit is the floor for a protocol holding funds, and two independent firms is common.
More from the journal

Decentralized Exchange Development: Architecture and Cost
A build guide for decentralized exchange development: how AMM, order-book and intent designs differ, what the architecture really contains, what a fork costs you in licence terms, and a cost model with its assumptions written down.

How to Create a Cryptocurrency: Coins, Tokens & Costs
Creating a cryptocurrency is three different projects wearing the same name. This guide separates them: a token on an existing chain, your own appchain, or a no-code launcher. With a working ERC-20, the 2026 rulebook in the EU and the US, and a costed model of each route.

Smart Contract Development Company: How to Choose One
A buyer's guide to picking a smart contract development company: a due diligence scorecard you can run yourself, how to read a deployed contract on a block explorer, and modelled build costs set against published audit prices.