Smart Contract Development Company: How to Choose One
A buyer's guide to picking a smart contract development company: a due diligence scorecard you can run yourself, how to read a deployed contract on a block explorer, and modelled build costs set against published audit prices.

On this page

A smart contract development company writes the on-chain code that holds and moves value, and builds the ordinary software around it: the app, the indexer, the admin tooling, the integrations that make the contract usable by people who don't read Solidity. Choosing one is a procurement problem with an unusual property. The work product is public. Every contract a firm has deployed sits on a block explorer with its source, its admin roles and its full transaction history, which means most of what a vendor claims in a pitch can be verified before you get on a second call.
This guide is the checking procedure: what the job covers, how a competent team runs a build, the scorecard to apply to a shortlist, how to read a deployed contract yourself, what the work costs against published audit prices, and the questions that separate a firm that has shipped from one that has read about shipping.
The short version
- A smart contract development company designs, writes, tests, audits and deploys on-chain code plus the off-chain product around it. A DeFi development company adds the financial design: interest and liquidation mechanics, collateral parameters, oracle choice, tokenomics and liquidity.
- The best signal isn't a client logo. It's a verified contract on mainnet whose admin roles, upgrade path and audit report you can inspect without permission.
- Build a scorecard before you take calls: audit track record, on-chain proof, security process, incident history, chain depth, engagement model, IP and key handover, references.
- Cost splits in two. Engineering runs from a few engineer-weeks for a single contract to a hundred or more for a protocol. Audits price separately, and Sherlock's published 2026 reference puts most DeFi protocol audits between 25,000 and 100,000 dollars.
- Anonymous teams, unverified contracts, the word "audited" without a linked report, fixed-price bids for undefined scope, and retained admin keys are the five red flags that predict the rest.
- There is no neutral ranking of the best firms. Directory rankings measure sales and service quality, not contract behavior under attack.
What a smart contract development company does
A smart contract development company turns financial or settlement logic into code that runs on a public blockchain, then builds and operates everything that logic needs to be a product. That is a broader job than the name suggests, and the contract itself is usually the smallest part of it by line count.
The work divides into five layers, and a firm can be strong in some and absent in others:
- Contract engineering. Solidity, Vyper or Rust, written small and deliberately boring, with checks-effects-interactions ordering, audited base libraries instead of hand-rolled access control, and upgrade paths that are explicit rather than accidental.
- Verification. Unit tests, fork tests, invariant and fuzz campaigns, static analysis, then an external audit. The Ethereum documentation on smart contract security is blunt about the division of labor: commissioning an audit is one way of conducting an independent code review, and it complements internal testing rather than replacing it.
- Off-chain infrastructure: indexers, keepers, RPC access, oracle integration, monitoring, and the APIs your front end and partners depend on. This is where most of the engineering hours go, which surprises almost every founder we scope with.
- Product and integration. The app people touch, wallet connection, transaction simulation, clear signing so users know what they're approving, and the admin tooling your operations team will live in.
- Deployment and operations, which is the layer teams discover they skipped: key ceremony, multisig setup, timelocks, staged rollout under deposit caps, incident runbooks written before the incident.
A DeFi development company is a smart contract development company with a financial design practice bolted on. The extra work is protocol economics: how interest accrues, what collateral factor keeps the system solvent through a sharp single-block price move, which oracle is used and how stale its price may get before the system pauses, how liquidations clear without cascading, and how tokens and liquidity are distributed at launch. Our breakdown of DeFi protocol types covers the categories that design work lives inside, and the wider state of decentralized finance piece has the measured context.
That distinction is worth more than it sounds. If your product holds other people's deposits and you hire a firm that only does the first list, you get code that compiles and a design that leaks.
Smart contract development company, in-house hire, or audit firm
These three aren't competing offers. They solve different problems, and picking the wrong one is the most expensive mistake in this whole process.
Hire in house when the contract is the product and you expect to keep changing it for years. Context stays with you, key custody stays with you, and the cost of a permanent senior engineer amortizes. The trap is hiring exactly one. A single contract engineer with deploy rights and nobody qualified to argue with them is the arrangement that produces incidents, and no amount of seniority fixes it. Budget for two, or for one plus a retained reviewer.
Hire a smart contract development company when you need a working team now, for a defined build, with the surrounding product included. You're buying assembled capability: a contract engineer, a backend engineer, a front-end engineer, someone who has run a deployment before, and a reviewer who wasn't in the room when the code was written. You're also buying the option to stop, which an employment contract doesn't give you.
Hire an audit firm when the code already exists and you need it attacked. An audit firm won't build for you, and a firm that both builds and audits its own work has removed the independence that made the audit worth buying. Our guide to what a smart contract audit covers goes through the process and the preparation that makes it cheaper.
For a first build the answer is usually a development company plus an independent audit firm, with the in-house hire arriving before the vendor leaves so someone on your payroll understands the code they inherit. If the real question is whether to build at all, our build versus buy analysis is the earlier conversation.
The build lifecycle a smart contract development company runs
A competent build runs in a fixed order, and the order is the thing to check. Ask a prospective vendor to describe their lifecycle before you describe yours, then listen for whether the stages line up with the ones below. A team that has shipped will name the gates. A team that has not will describe a process without any.
Design and invariants. Parameters get decided before code exists: supported assets, price sources and staleness tolerance, collateral factors, fee routing, and what must always be true no matter what sequence of transactions arrives. Those invariants become the fuzzing targets later, which is why writing them down first is engineering, not documentation.
Implementation. Small contracts, audited libraries, minimal privileged surface. The engineering detail behind each pattern, including vault share accounting, AMM pricing and the re-entrancy and oracle pitfalls that keep draining protocols, is covered in our DeFi smart contracts engineering guide; there's no point repeating it here.
Layered testing. Unit tests prove the code does what the author expected. Fork tests prove it works against real deployed dependencies. Invariant and fuzz campaigns throw sequences nobody imagined at the contracts and check the properties still hold. Formal verification goes further where the value justifies it, and the Ethereum docs are precise about why it's different: it can conclusively prove the absence of a class of errors, which no test suite can.
External audit and remediation. Code freeze, tagged commit, audit, findings, fixes, re-review. Two firms for anything ambitious, because different methodologies surface different classes of issue.
Deployment and operations. Multisig and timelock in place before mainnet, staged rollout under deposit caps, monitoring on anomalous flows, an incident plan written while nobody is panicking.
What a senior smart contract development team looks like
A senior team assembled for that lifecycle has at least four roles: a contract engineer who owns the on-chain surface, a protocol or product engineer who owns everything off-chain, a reviewer who didn't write the code and holds a veto at each gate, and someone accountable for keys and deployment. Ask which named person holds each role on your project. "The team handles it" means nobody does.
A due diligence scorecard for smart contract development companies
Score every shortlisted firm on the same eight checks, and do it before you fall in love with a proposal. The right-hand column is the part that matters, because each check has a verification path that doesn't depend on the vendor's cooperation.
Audit track record is the check people fake most often, and it's also the easiest to test, because reputable auditors publish. Trail of Bits keeps its security reviews in a public repository covering well over a hundred engagements across protocols, wallets and cryptographic libraries. If a vendor names an auditor, the report should be findable at the auditor's end.
Red flags that should end the conversation
The red flags are shorter and mostly binary. Any one of these is a reason to stop rather than to negotiate:
- An anonymous team. Pseudonymity is normal for protocol contributors and abnormal for a vendor you're wiring money to.
- No verified contracts. Publishing and verifying source on an explorer is free and takes about ten minutes. Skipping it is a choice, not an oversight.
- "Audited" with no linked report. A badge isn't a document. A report without the commit hash it covered is decorative, because it can't be matched to running code.
- A fixed-price bid for undefined scope. Nobody can price a system they haven't scoped. A firm that does it either hasn't read your brief or intends to renegotiate later.
- Admin keys retained after handover. If the vendor still holds the upgrade key when the engagement ends, they can still change your product, and a contract clause won't stop a signed transaction.
A vendor's reaction to a handover checklist during the sales call tells you more than anything in the proposal.
How to check if a smart contract is legit
You can run this yourself in about fifteen minutes per address. Do it, because it's the same procedure you'll use on your own vendor's output later, and it's easier to learn on a contract you have no money in.
Start with source verification. Etherscan's own definition is exact: contract verification lets developers prove and publish the source code of contracts deployed on-chain. It also distinguishes four states, and the distinction is load-bearing. An exact match confirms the deployed code and its constructor arguments. A similar match only means the bytecode resembles another verified contract and ignores constructor arguments, which is where a token with different parameters can hide behind a familiar-looking name. Unverified means you're looking at bytecode and taking someone's word for the rest.
Read the privileged roles. Who is the owner? Who can mint, pause, set fees, change the oracle, or move funds? Then look at what those addresses actually are. An externally owned account is one private key away from being the attacker. A multisig at least requires collusion or multiple compromises, and the Ethereum security docs make the point plainly: multisig accounts add a layer because actions need consent from more than one party.
Check whether it's a proxy. If it is, the address you trust is a shell that forwards calls to an implementation somewhere else, and whoever controls the admin can swap that implementation. In OpenZeppelin's transparent proxy pattern, a ProxyAdmin contract holds that power and only the admin can upgrade. Find out who controls the ProxyAdmin, because that's the real owner of the product.
Then look for a timelock, which puts a mandatory delay between an approved change and its execution. OpenZeppelin's governance documentation gives the reason in one sentence: it is good practice to add a timelock to governance decisions, because it allows users to exit the system if they disagree with a decision before it is executed. No timelock on a contract holding deposits means an upgrade can land while you sleep.
Match the audit to the code. Get the report, find the commit hash it covered, and compare that against the verified source. A report written against a commit that no longer resembles what is deployed tells you about a codebase that stopped existing.
One last check, on your own side: token approvals are the quiet risk. Granting an unlimited allowance to a contract means it can move that token from your wallet at any point in the future, including after an upgrade you didn't read. Review and revoke approvals you no longer use.
What these smart contract checks cannot tell you
What none of this proves is that the contract is safe. It proves the claims are checkable, and a project that fails these checks has told you something before you've read a line of its logic. Our wider blockchain security guide covers the threat model these checks sit inside.
What it costs to hire a smart contract development company
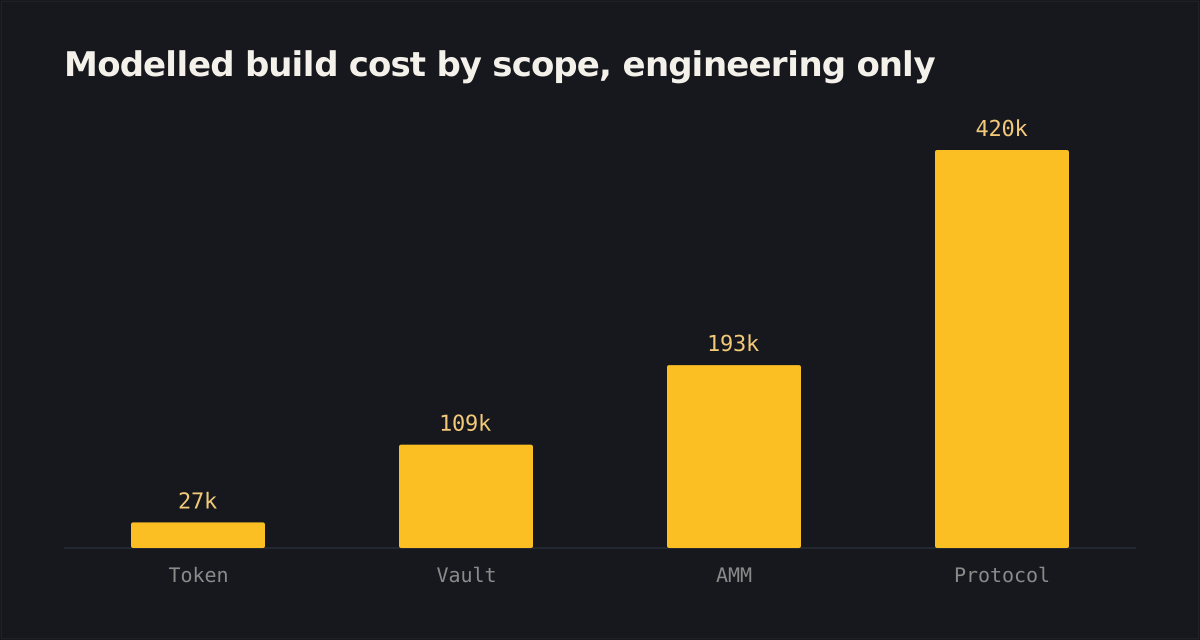
Cost splits into engineering and security, and mixing the two is how budgets go wrong.
The engineering side is a model you can rebuild with your own numbers, which is the only honest way to publish one. Ours assumes a single EVM chain, a blended rate of 110 dollars an hour across contract, backend and front-end engineering, and 38 billable hours a week, so roughly 4,200 dollars per engineer-week. Engineer-weeks are summed across the squad, not calendar weeks. Audit fees, bug bounty, legal, token design and go-to-market all sit outside these figures.
Swap the rate for whatever your market charges and the ratios hold. The week counts are the part worth arguing about, and a vendor who can't defend theirs line by line is guessing.
Engagement models, and when each one fits
Three engagement models cover almost every build, and the choice matters more than the hourly number most buyers ask about first:
A first build almost always belongs in the first row: you get the number before the commitment, and the vendor carries the risk of having estimated it wrong. If you want the engagement-model question answered across our whole practice rather than just contract work, our dedicated development team and software development consulting pages set out how we structure each.
What a smart contract audit costs, from published prices
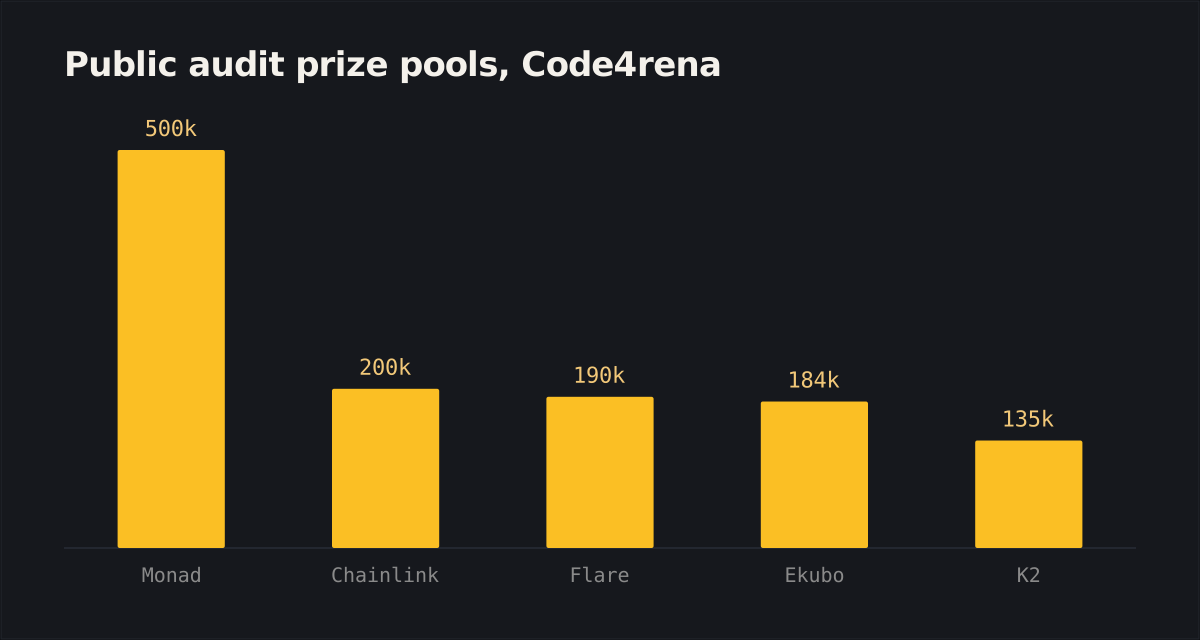
Audits are the one part of this market that prices itself in public, which makes them the anchor for the rest of your budget. Sherlock published a 2026 market reference for audit pricing on 18 February 2026: engagements run from 5,000 to 250,000 dollars, with most DeFi protocol audits landing between 25,000 and 100,000. A simple token sits at 5,000 to 20,000. A mid-complexity DeFi protocol is 40,000 to 100,000, or 60,000 to 120,000 once at least one remediation review is included. Enterprise multi-chain systems routinely exceed 150,000. Each re-audit pass after remediation adds 5,000 to 20,000. Sherlock also notes that protocols with meaningful value locked run annual security budgets of 150,000 to 500,000 dollars, which is the number nobody puts in a launch plan.
Competitive audits publish their prices too. Code4rena lists the prize pool for every competition it runs, and the range on the board when we captured it on 10 September 2026 ran from 4,000 dollars for a small mitigation review to 500,000 for the Monad layer-one competition. Chainlink Rewards ran at 200,000, Flare FAsset at 190,000, Ekubo at 183,500, and K2 at 135,000. Read those as the cost of having independent researchers attack one codebase once, not as a substitute for a firm audit.
Bug bounties are the third layer and they scale differently. The Immunefi Foundation's May 2026 ecosystem update reported 138.5 million dollars in all-time researcher payouts, up from 133.9 million in March. The Ethereum security guidance suggests setting a bounty in proportion to the funds at stake, which is the same logic as the audit budget: the security spend tracks the value the contract will hold, not the size of the codebase.
Set against that, DeFiLlama's hacks database recorded 1.82 billion dollars stolen between 1 January and 9 September 2026 across 257 incidents, of which 183 incidents and 1.15 billion dollars hit DeFi protocols directly. Access control failures accounted for 367 million and key compromise for 308 million of that total. Neither of those categories is a complexity problem. They're process problems, which is exactly what you're buying when you pay for a senior team rather than a cheap one.
Where the top smart contract development companies are
The short answer: geography is a weak signal, and the rankings you'll find aren't measuring what you need measured.
Serious contract engineering is distributed. The deepest public track records sit in North America, Western and Eastern Europe, and increasingly in Singapore and the UAE, and the reason isn't local talent density. This discipline grew up in open source, so the people who are good at it are visible through their commits, their audit findings and their deployed contracts rather than through an office address. A firm in Tallinn with fifteen verified mainnet contracts beats a firm in San Francisco with none.
Directory rankings are worth understanding before you lean on them. Clutch builds its Leaders Matrix from verified client feedback, project track record and market presence, plotted on axes of focus and ability to deliver. That is a reasonable measure of how well a firm sells, scopes and services clients. It isn't a measure of how a contract behaves when a well-funded attacker reads it, and no directory claims otherwise. Use directories to find candidates, then run the scorecard above to eliminate them.
We maintain our own compared list of blockchain development companies, which leaves us off the ranking and says so, and which names the firms whose claims we could not verify rather than quietly dropping them. Treat it the same way: a source of candidates, not a verdict. If you want the broader stack context before shortlisting anyone, our web3 development guide covers what the surrounding system has to include.
Questions to ask a smart contract development company on the first call
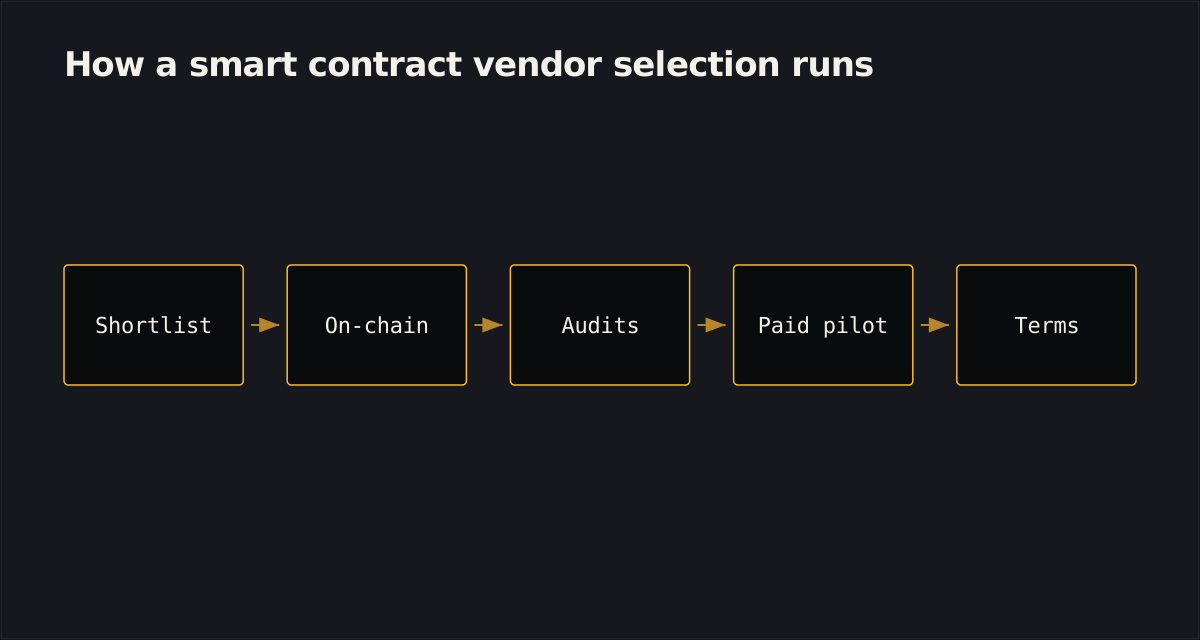
Treat the first call as a filter rather than a briefing. Spend it asking, and listen for whether each answer is specific or rehearsed.
That last row is the one worth weighting. A firm with real production exposure and no incident is either very lucky or very new. A team that has walked through a bad week and changed its process afterwards is usually safer than one that's never been tested. Defensiveness about findings is the strongest negative signal in this whole list.
Expect the shortlist-to-contract process itself to take three to five weeks: a week of on-chain checking, a week of calls, a paid discovery or pilot of one to two weeks, then terms. Compress it to a week and you skipped the part that was supposed to protect you.
What Idealogic builds, and what we do not
We're a smart contract development company in the first sense of this article. We design and build contract systems and the products around them, and we commission third-party audits rather than performing them, because a firm auditing its own code isn't an audit. Two things we won't say: we don't call any contract unhackable, and we don't claim regulatory status on a client's behalf.
The work is easier to judge in specifics. SeedBox is a crypto venture-investing platform we built from a written product requirement document to a live MVP: Solidity contracts with Ethers.js and Web3.js, a React front end over an AdonisJS and PostgreSQL backend, individual investor wallets, KYC-checked onboarding, fiat and crypto rails in one flow, dynamic investment pools with tier rules, and token-holder governance. The design call worth naming is the on-chain and off-chain split. Contracts hold what has to be trustless; investor profiles, KYC status, tier assignments and pool metadata stay in PostgreSQL where they are queryable and fast. That keeps the contract surface small, which is its own kind of safety.
Zert is an escrow-first product where contract code settles the deal: funds lock into an escrow account, the agreed conditions live in the contract, settlement executes on its own when they are met, and the outcome is release or refund with no path to limbo. Multi-sig sits in the custody layer, so one compromised credential can't move funds. None of that machinery is exposed to the user, which was the harder half of the build.
Planetcoin is a centralized exchange for first-time buyers: card-to-crypto onboarding, fees shown before the buy is confirmed, a dashboard readable without trading fluency, web and mobile by one squad. Glue trades crypto against gold as the base asset, with a supply-and-borrow lending side and a no-hidden-fee policy carried into the interface.
That is the range, with the blockchain development practice supplying the on-chain layer and the rest of the house supplying the app around it.
Choosing a smart contract development company without guessing
Every check in this article exists to convert a bet into something you can verify: an address, a commit hash, a report, a key, a named role. Choosing a smart contract development company is still a judgment call about people you've met for a few hours, but the share of that judgment resting on trust should be small, and it's entirely within your control to make it smaller.
Run the scorecard and open the addresses yourself. Then ask for the difficult reference, the one about a project that went badly. Price the audit as a separate line before you compare quotes, because a proposal without one isn't cheaper, it's incomplete. And settle the handover terms while you still have bargaining power, because a key held by someone else after the invoice is paid is the one problem no contract clause solves quickly.
If you're scoping a build and want a smart contract development company that works to that standard from the first sprint, start the conversation before any code exists.
CEO and Co-founder at Idealogic. Leading software strategy, systems architecture, and AI-native engineering squads since 2016.
Frequently asked questions
A smart contract developer writes, tests and deploys the on-chain code that holds and moves value, usually in Solidity, Vyper or Rust. The job is narrower and slower than ordinary backend work: the code is public, it can't be hot-fixed once deployed, and every function has to survive an attacker who has read it. Day to day that means specifying invariants before writing code, building on audited libraries, writing fuzz and fork tests, running static analysis, preparing the codebase for external audit, and handling deployment, admin roles and monitoring afterwards.
Start on a block explorer. Confirm the source is verified as an exact match rather than a similar match, since a similar match ignores constructor arguments and a token with different parameters can hide behind a familiar name. Read who holds the owner and admin roles, and whether those addresses are single keys or a multisig. Check whether the contract is a proxy, because whoever controls the proxy admin can replace the logic behind an address you already trust. Look for a timelock, which is what gives holders time to exit before a change lands. Then match the audit report's commit hash to the deployed source. None of this proves a contract is safe. It proves the claims are checkable, and each missing piece is a reason to stop.
There is no neutral ranking, and any list that presents one is usually a marketing page. Directories such as Clutch build their Leaders Matrix from verified client feedback, project track record and market presence, which measures how well a firm sells and services clients rather than how its contracts behave under attack. The more useful move is to build your own shortlist from public evidence: verified contracts on mainnet, published audit reports naming the firm, and open-source repositories. Geography matters far less than whether the code is checkable.
A single standard token or standalone contract is a few engineer-weeks of work, and Sherlock's published 2026 pricing puts an audit for one at 5,000 to 20,000 dollars. A vault, staking contract or lending market is a different order of magnitude: tens of engineer-weeks of build, plus 40,000 to 100,000 dollars for a mid-complexity DeFi audit. Enterprise multi-chain systems routinely exceed 150,000 dollars in audit fees alone. Any quote that omits the audit line is quoting half the project.
A smart contract development company builds and ships contract code, which may be a token, an escrow, an NFT collection or a piece of enterprise settlement logic. A DeFi development company does that plus the financial design around it: interest and liquidation mechanics, collateral parameters, oracle selection, tokenomics, liquidity bootstrapping and the economic stress-testing that decides whether the protocol stays solvent. If your product holds other people's deposits, you need the second set of skills even if you only advertise the first.
In house wins when the contract is the product and you expect to keep changing it for years. An agency wins when you need a senior team now, for a defined build, with the app around it included. The failure case is hiring one engineer and no reviewer, because a single person with deploy rights and nobody to argue with is the arrangement that produces incidents.
Three to five weeks for a single standard contract, eight to twelve for a vault or staking product, fourteen to twenty for an AMM or lending market, and half a year or more for a full protocol. Audits add calendar time on top, since good firms book weeks ahead and re-review is a second pass.
Yes, and a simple contract makes it cheap. Sherlock's published range for a standard token audit is 5,000 to 20,000 dollars, which is small against what the contract will hold. Simplicity also doesn't protect you from the failure classes that dominate the loss data: access control and key compromise together account for roughly 675 million dollars of the 1.82 billion dollars DeFiLlama tracked in 2026 through 9 September, and neither of those is a complexity problem.
More from the journal

Decentralized Exchange Development: Architecture and Cost
A build guide for decentralized exchange development: how AMM, order-book and intent designs differ, what the architecture really contains, what a fork costs you in licence terms, and a cost model with its assumptions written down.

Smart Contract Development: Lifecycle, Patterns, Cost
Smart contract development is mostly verification, not typing. This guide walks the lifecycle from specification to monitoring, with Solidity code, a language and chain comparison, exploit losses measured from DeFiLlama, and what an audited build costs.

Top 10 Custom Software Development Companies in 2026
Ten custom software development companies worth a shortlist in 2026, ordered by scale rather than by who paid for the placement. Plus the five firm archetypes, the evaluation checks that matter, and what each engagement model really costs.