Crypto Wallet App Development: Architecture, Security, Cost
A wallet holds keys, not coins, so key handling decides the architecture, the security budget and whether you need a licence. Custody models, the component architecture, measured theft data, the MiCA and FinCEN thresholds, and a cost model in engineer-weeks.

On this page

Crypto wallet app development is the work of building software that generates private keys, keeps them out of reach, and uses them to sign blockchain transactions. Notice what that sentence leaves out. The coins are never in the app. They sit on a public ledger, and the wallet holds the one credential that can move them. That fact decides the architecture, the security budget, and whether you need a licence to ship.
This guide is the build angle. For the full taxonomy of wallet formats, our explainer on the types of digital wallets covers hardware, paper, smart-contract and everything between. Here we stay with the engineering: the components, the tooling that is current in 2026, the attacks that actually take money, the regulatory line custody draws, and a cost model you can argue with because the assumptions are written down.
The short version
- A wallet holds keys, not coins, so key generation, key storage, signing, chain integration and recovery are the five parts that carry the build.
- Three decisions set almost everything downstream: custodial or non-custodial or MPC, single-chain or multi-chain, and mobile or web or browser extension.
- Device hardware does the heavy lifting for self-custody. The iOS Secure Enclave and the Android Keystore both keep key material out of your app's process entirely.
- Chainalysis counted over $3.4 billion stolen across crypto in 2025, of which $713 million came from personal wallet compromises across 158,000 incidents.
- Custody is the regulatory trigger. MiCA Recital 83 puts non-custodial wallet software outside the Regulation; FinCEN reached the same conclusion for unhosted single-signature wallets in 2019.
- Our model puts a single-chain non-custodial MVP at 22 to 30 engineer-weeks and a custodial or MPC product with a compliance perimeter at 90 to 120.
What crypto wallet app development involves
Crypto wallet app development involves five concerns, and each one constrains the next. You generate a key from strong entropy. You store it where nothing else on the device can read it. You build and sign transactions without the key leaving its boundary. You talk to a chain to read balances and broadcast. And you give the owner a way back in when the phone goes in a river.
None of those is a screen. The interface matters, because a confusing wallet is one people hesitate to use with real money, but the dangerous engineering sits underneath it.
Before any of that, three product decisions set the shape of the build. They're cheap to change in week one and brutal to change in month six, which is why we force them out of a client during discovery.
The custody row is the expensive one. It decides whether you're a software vendor or a regulated financial business, and no amount of clever engineering later will move that line.
Chains are where teams underestimate the work. Adding a second EVM chain is configuration. Adding Solana or Bitcoin is a second signing path, a second address format, a second fee model and a second set of edge cases in your test suite. The surface row decides how good your key storage can be: a phone gives you hardware isolation for free, while a browser extension gives you an origin sandbox and little else.
Wallet types and the trade-offs that pick one
Wallet types sort along two independent axes. Connectivity asks whether the signing key ever touches an internet-connected device, the hot and cold split. Control asks who holds the key. A custodian can keep keys in cold storage, and a self-custody wallet can be blisteringly hot.
Below is the scoping version: each row points at a different security model and a different chunk of engineering, which is what matters when you're estimating.
Two honest notes on that grid. Custodial doesn't mean safe and non-custodial doesn't mean risky; several of the largest losses in crypto were custodial failures rather than protocol ones. And there's no best row: plenty of products run a non-custodial wallet for users while operating a hot float and cold reserves behind the scenes.
Crypto wallet architecture, component by component
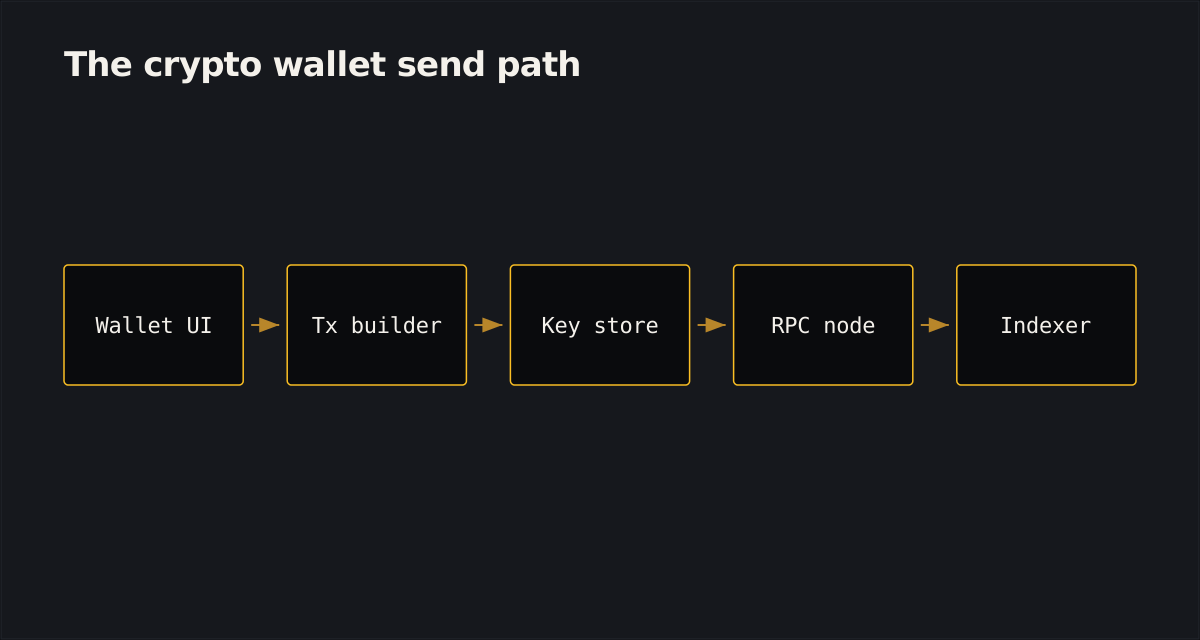
A crypto wallet app is a signing device wrapped in a chain client. The path below is what a send traverses, and each stop is a place where a design decision either protects the user or quietly exposes them.
Key generation and storage
Everything starts with entropy. You generate a cryptographically secure random seed, encode it as a mnemonic, then derive a key tree from it. The standards are settled, and you shouldn't deviate from them. BIP-39 takes 128 to 256 bits of entropy, appends a SHA-256 checksum, maps the result to 12 through 24 words, then runs PBKDF2 with HMAC-SHA512 and 2,048 iterations to produce a 512-bit seed. BIP-32 turns that seed into a hierarchy, and BIP-44 fixes the path shape as m / purpose' / coin_type' / account' / change / address_index so that one phrase restores every chain the wallet supports.
Where the derived key lives is the decision that separates a serious wallet from a liability. On iOS, the Secure Enclave is a separate hardware subsystem, and Apple's own documentation is blunt about the boundary: keys "stay within the AES Engine and aren't made visible even to sepOS software". On Android, the Keystore system carries the same guarantee at the OS level, stating that "key material never enters the application process", with StrongBox adding a discrete secure element that has its own CPU, its own storage and its own random-number generator. If your app can print the private key to a log, you've already lost the argument.
For shared or business control, remove the single key altogether. Threshold signing splits key material into shares so the whole key is never assembled, even during a signature. Fireblocks states the property directly, that "the complete key is never assembled in one place, at any point in time", and claims its MPC-CMP protocol cuts signing from the nine rounds of the earlier GG18 protocol to one. Turnkey takes the enclave route instead, saying keys are "secured in hardware-isolated enclaves and never exposed, not even to Turnkey". Coinbase Developer Platform offers embedded wallets whose users can export their keys, with API-key wallets handled "inside a Trusted Execution Environment", and Dfns sells the same shape to regulated institutions. All four remove a category of work from your backlog and add a vendor to your threat model. Fair warning: that swap is the fastest way to ship and the hardest call to reverse, because your recovery story becomes theirs.
Transaction building and signing
Building a transaction is chain-specific bookkeeping: fetch the nonce or recent blockhash, estimate the fee, encode the call data, assemble the payload. Signing is the moment the key is used, and it belongs inside the storage boundary. On mobile that means asking the enclave to sign, never asking it for the key.
That signing screen is a security control in its own right. Most wallet losses come from a user approving something they didn't understand rather than from broken cryptography, so decode the call data into a human sentence, show the asset movement, and never render an opaque hex blob with an Approve button next to it.
Nodes, RPC providers and indexing
A wallet needs to read chain state and broadcast transactions, and almost nobody runs their own nodes at the start. Managed RPC is a line item you can price today. Alchemy publishes a free tier of 30 million compute units a month and pay-as-you-go at $0.45 per million CU for the first 300 million, dropping to $0.40 after. QuickNode lists Build at $49 a month for 80 million API credits and Accelerate at $249 for 450 million.
Balances and history are a separate problem. Reading them straight from RPC is slow and expensive, so production wallets sit behind an indexer holding token balances, transfer history and NFT data. Teams that skip this find out when the portfolio screen crawls on a wallet holding thirty tokens.
Swaps, on-ramps and dapp connections
Three integrations turn a key manager into a product people use. Swap routing through an aggregator such as 0x or 1inch lets users trade without leaving the app. A fiat on-ramp such as MoonPay or Transak lets ordinary money in, with the provider carrying the identity checks for its own markets. WalletConnect, now shipped through Reown as AppKit and the WalletConnect SDK, is how your wallet reaches the dapp ecosystem.
Each is also an attack surface. A swap route is a contract call your user approves, an on-ramp is a third party inside your onboarding funnel, and a dapp session is a channel through which arbitrary signature requests arrive. Treat all three as untrusted input.
Account abstraction: ERC-4337 and EIP-7702
Account abstraction changes what a wallet can offer, and both standards are now Final rather than speculative. ERC-4337 specifies smart accounts with custom validation logic through a separate UserOperation mempool and bundlers, and it "completely avoids the need for consensus-layer protocol changes". EIP-7702, titled Set Code for EOAs, shipped in the Pectra upgrade on Ethereum mainnet on 7 May 2025 and lets an ordinary account delegate its behaviour to contract code.
What that buys: transaction batching, sponsored gas so a first-time user doesn't need the native token, session keys, and recovery that doesn't depend on a written phrase. What it costs: a second execution path to test, bundler or paymaster infrastructure to run or rent, and a new class of signature to explain on the approval screen. That last point isn't theoretical, as the security section shows.
The crypto wallet app development tech stack
There's no single correct stack, but there is a current one. The table below is what we reach for by default and the condition under which we pick something else.
React Native is the default because the crypto-specific work is mostly native module glue, and one codebase halves the QA matrix for a wallet that has to behave identically on both platforms. Our React Native and Flutter practices both ship wallets; the choice is usually a team question rather than a technical one.
The rule that outranks the whole table: never roll your own crypto. Use reviewed, widely deployed libraries for derivation, signing and encryption. Homegrown cryptography passes every test you write for it and fails in production against an adversary who is better at this than your test suite.
Crypto wallet security: the threats and the controls
Wallet security reduces to one question asked at every layer: who can reach the private key, and what can they get the owner to sign? The first half is engineering. The second half is where the money goes.
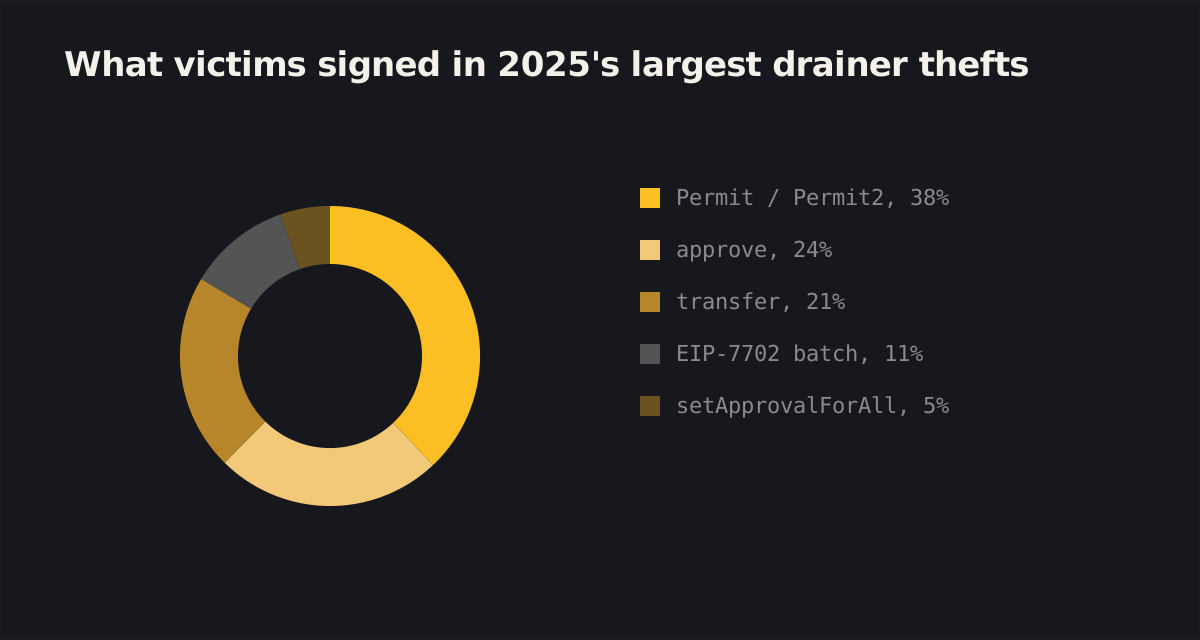
The 2025 numbers reward reading carefully. Chainalysis counted over $3.4 billion stolen between January and early December 2025, with the February Bybit compromise alone accounting for $1.5 billion of it. Personal wallet compromises came to $713 million across 158,000 incidents affecting at least 80,000 unique victims, which is 20 percent of all value stolen on their lower-bound estimate, down from 44 percent in 2024. Private key compromise at centralized services remains the heavyweight when it happens: Chainalysis attributes 88 percent of first-quarter 2025 losses to it.
Drainer phishing, the attack that hits ordinary wallet users, fell sharply. Scam Sniffer recorded $83.85 million lost across 106,106 victims in 2025, down 83 percent and 68 percent respectively from 2024's $494 million and 332,000 victims. The composition is the actionable part. Across the eleven thefts of $1 million or more, permit and Permit2 signatures accounted for 38 percent of the value, approve and increaseApproval 24 percent, plain transfers 21 percent, and EIP-7702 batch signatures 11 percent, an attack class that didn't exist before Pectra shipped in May.
A wallet is only as safe as the worst place its private key has ever existed, and only as safe as the worst thing it has ever asked a user to sign without explaining it.
The threat model your wallet has to survive
Five attacks account for most of what goes wrong, and none of them require breaking a curve.
- Signature phishing. The user is shown a plausible site and asked to sign a permit message, an off-chain signature that grants an allowance without any transaction from the token holder. Nothing leaves the wallet at signing time, so the usual mental model of "I didn't send anything" fails. Largest category in the chart above.
- Malicious approvals. Same idea through an on-chain approve or setApprovalForAll, which hands a contract unlimited authority over a token or an entire NFT collection until it's revoked.
- Seed phrase capture, still the classic. Fake support agents, cloud-backed screenshots, phishing restore screens. Those 12 words are the funds, so every UX decision around them is a security decision.
- Device and clipboard compromise. Malware that swaps a copied address, reads plaintext storage, or overlays the approval screen. Hardware-backed key storage neutralises the extraction half of this; it doesn't neutralise the deception half.
- Supply chain: a compromised npm dependency, a malicious SDK update, a poisoned build. Your wallet ships the attacker's code straight onto the device holding the keys, which turns dependency review from a chore into a security control.
The controls that move those numbers
Given that list, the controls that matter are the unglamorous ones.
- Decode before you ask. Simulate the transaction and render the actual asset movement in plain language, including allowance changes. If your signing screen can't explain a permit message, your users can't either.
- Hardware-backed keys by default: Secure Enclave, or Keystore with StrongBox where the device has it. Never a key in app memory for longer than a signature takes.
- Allowance hygiene as a feature. Show live approvals, flag the unlimited ones, make revocation a single tap. Most wallets bury this and their users pay for it.
- Recovery that doesn't depend on paper. Social recovery, MPC share rotation, guardians on a smart account. A recovery model people finish beats a stronger one they skip, and Swissy's numbers below back that up.
- Audits and a pen test before real money. Anything with contract code needs an external audit and the whole app needs a mobile penetration test. Our guides to blockchain security and the smart contract audit process cover what those engagements should include.
- Dependency discipline, which is the one nobody wants to own: pinned versions, lockfile review, reproducible builds, and a named human who approves SDK upgrades.
When a crypto wallet app needs a licence
Whether you need a licence turns on one question: do you control the keys? The position below reflects the rules in force as of September 2026, and it's a starting map rather than legal advice for your jurisdiction.
In the European Union, MiCA has applied since 30 December 2024 under Article 149(2). Article 3(1)(17) defines the regulated service as "the safekeeping or controlling, on behalf of clients, of crypto-assets or of the means of access to such crypto-assets, where applicable in the form of private cryptographic keys", which is custody described precisely enough to test your own design against. Provide it professionally and you need authorisation as a crypto-asset service provider. Recital 83 draws the other side of the line in one sentence: "Hardware or software providers of non-custodial wallets should not fall within the scope of this Regulation." Recital 22 adds that services provided in a fully decentralised manner without any intermediary are outside scope too.
The EU Travel Rule is a separate instrument, Regulation (EU) 2023/1113, applying from the same date. It reaches every transfer of crypto-assets, including those to and from a self-hosted address, "as long as there is a crypto-asset service provider involved", and there's no de minimis threshold on the information requirement. Above EUR 1,000 to or from a self-hosted address, the service provider must verify that the address is owned or controlled by its client. If your product has any custodial leg, this becomes an engineering requirement rather than a policy document.
In the United States, FinCEN guidance FIN-2019-G001, issued 9 May 2019, applies four criteria: who owns the value, where it's stored, whether the owner interacts directly with the payment system, and whether the intermediary has total independent control over the value. Hosted wallet providers are "account-based money transmitters" and register as money services businesses. For unhosted single-signature wallets the guidance concludes the opposite, since the owner interacts with the payment system directly and has total independent control. Multi-signature providers that only add a second authorisation key aren't money transmitters either. Combine that with hosted wallet services, though, and you are.
The US Travel Rule sits at 31 CFR 1010.410, which applies recordkeeping and transmittal requirements to non-bank financial institutions for transmittals of $3,000 or more. Note the threshold difference from the EU. Note too that the rule binds the transmitting institution, which is you only if your product has a custodial leg.
For a product team the consequence is simple. If the roadmap has a phase where you start holding user funds, the licence, the AML programme and the audit trail belong in that phase's estimate. Teams that discover this after launch end up rebuilding onboarding.
Crypto wallet app development cost and timeline
Cost tracks the custody and security model far more than the screen count. Below is a model, not a quote. The engineer-weeks come from wallet builds we've shipped; the dollar figures apply a blended $60 an hour, which is where a senior Central and Eastern European squad sits. Swap in your own rate and the engineer-weeks hold.
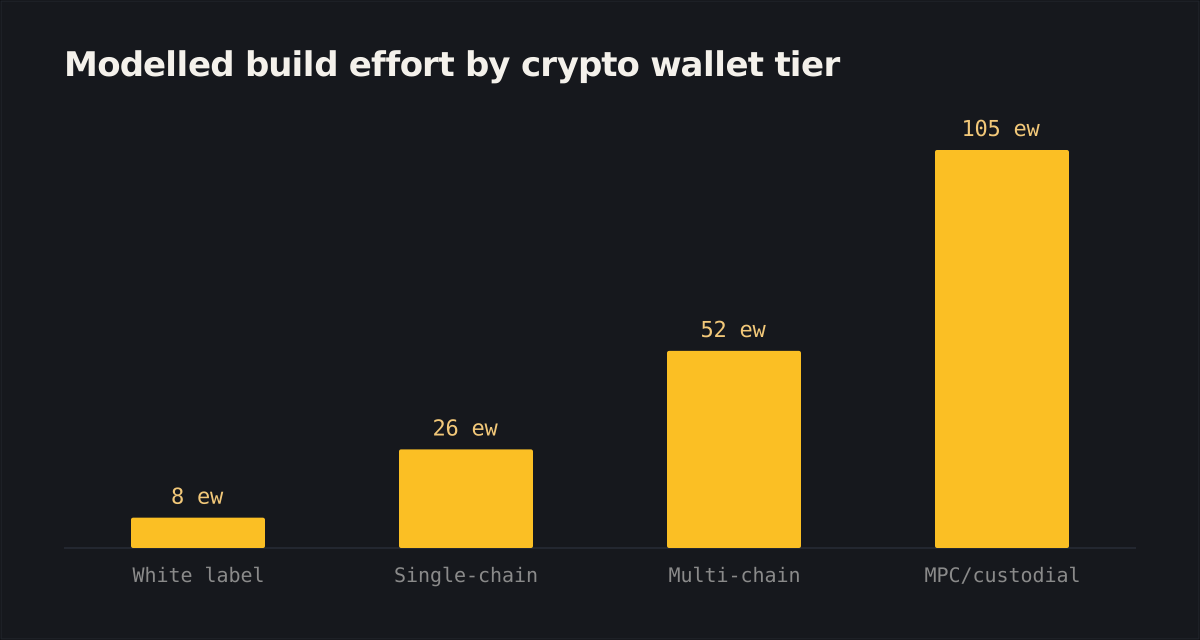
Here are the assumptions, so you can adjust them honestly. Every tier includes product design, a mobile build for both platforms, backend, QA and store release. None includes an external security audit, a penetration test, legal and licensing work, or a launch campaign. The single-chain MVP covers one EVM chain, seed-phrase or social recovery, send and receive, and a portfolio view. The multi-chain tier adds one non-EVM chain, which is where the second signing path lands. The custodial tier covers a hot and cold treasury split, an AML programme and Travel Rule messaging, but not the licence itself.
White label crypto wallet versus custom build
A white label crypto wallet gives you a branded app in weeks, which is a real advantage when the wallet is a distribution channel for something else, or when you're testing demand before committing engineering.
Costs show up later. The vendor's chain list becomes yours. Custom signing flows, unusual recovery models and specific dapp integrations are limited to what the platform exposes. The security posture is inherited, so you're trusting someone else's key handling with your brand on the icon. Build custom when the wallet is the product, when key handling is your differentiator, or when regulation forces the perimeter inside your own walls.
What a crypto wallet costs to run after launch
Run costs are easier to price than most teams expect, because the vendors publish them.
- RPC and indexing. Alchemy's free tier covers 30 million compute units a month, and pay-as-you-go runs $0.45 per million after that. QuickNode's Build plan is $49 a month for 80 million credits, Accelerate $249 for 450 million. A busy portfolio screen burns through more than founders expect, because every balance refresh is a read.
- Key infrastructure. Turnkey publishes $0.10 per signature on pay-as-you-go with up to 1,000 free wallets, $0.05 on a $99 monthly Pro plan, and as low as $0.0015 at enterprise volume. Fireblocks and Dfns quote rather than publish.
- Ongoing security: re-audit after any change to signing or contract code, and budget an annual penetration test.
- Then the ordinary running costs. App store fees, crash reporting, push infrastructure, plus transaction monitoring and reporting for anything custodial.
How to build a crypto wallet, step by step
Here's the order we run. It differs from most published guides because the security and compliance work starts at the beginning rather than the end.
- Fix custody, chains and surface. Write the three decisions down and get them signed. Every later estimate depends on them.
- Write the threat model before the architecture. List the assets, the adversaries and the trust boundaries. It takes a day and it changes the design.
- Choose the key-management approach. Device keystore, an infrastructure vendor, or your own threshold scheme. Prototype the signing path first, because it's the riskiest part.
- Build derivation and storage against the standards. BIP-39 mnemonic, BIP-32 tree, BIP-44 paths, hardware-backed storage, restore tested on a wiped device.
- Ship the send path end to end on a testnet: build, sign, broadcast, confirm, reconcile. One chain, no features, fully working. This is the milestone worth celebrating, not the first screen.
- Design the approval screen as a security control. Simulate, decode, show asset movement and allowance changes in plain language.
- Add balances and history through an indexer, then the portfolio view, which is the screen people open most.
- Layer on swaps, on-ramp and WalletConnect. Each behind a feature flag, each with its own failure states in the UI.
- Recovery, then hardening: social recovery or guardians, allowance management, jailbreak and root detection, certificate pinning. The common mistake here is treating recovery as a settings screen instead of an onboarding step.
- External audit and penetration test, then release. Book the audit slot early; the good firms have queues.
Can you create your own crypto wallet app
Yes, with a caveat that decides everything. A non-custodial, single-chain mobile wallet is a realistic build for a competent team: the derivation standards are published, the platform gives you hardware key storage, and the chain client is a library away. Steps four and five are where you'll spend the time, and that's the right place to spend it.
The caveat is custody. The moment you hold someone else's keys, you're not shipping an app, you're operating a financial business with the licensing, AML and audit obligations that come with it. Learn on a wallet where the user holds the key. Bring in people who've done custody before you build one that holds funds.
Launch checklist
Two crypto wallets we shipped, and what they proved
We've taken this route twice, from opposite ends of the design space.
Swissy is a non-custodial mobile wallet on iOS and Android where the private key is generated inside the device secure enclave and never leaves it, biometrics gate every sensitive action, and social recovery replaces the seed phrase by splitting encrypted key fragments across trusted contacts. The case reports a 4.6-star rating across both stores, 89 percent download-to-active-wallet onboarding completion, 41 percent of users making a first crypto purchase through the in-app on-ramp in month one, and 67 percent configuring social-recovery guardians within thirty days. That last number is the interesting one: recovery went from a step people skip to a step people finish, which is exactly what the security section above argues for.
Kanso went the other way. It's a multi-currency wallet for web and mobile built design-first, with real-time portfolio valuation as the home screen and multi-factor authentication and encryption underneath. The thesis was that in a category where wallets compete on feature lists and end up looking like the list, the one people enjoy opening wins.
Two wallets, two theses, one discipline about where the key lives. Our blockchain development practice covers the wider view, and our roundup of blockchain development companies is a fair place to start comparing partners, us included.
Where to start with crypto wallet app development
Start with the three decisions, because crypto wallet app development is downstream of all of them. Custody sets your licensing exposure and audit scope, the chain list sets your signing code and QA matrix, and the surface sets how good your key storage can be. Freeze those and the estimate stops moving.
Then build the send path before the product. A wallet that can derive a key, sign correctly, broadcast and reconcile on one chain is most of the hard work; what follows is addition rather than rework. Teams that ship late are usually the ones that built twelve screens first. For the surrounding context, our guides to web3 development, decentralized applications, DeFi and crypto exchange features and revenue models cover the systems a wallet ends up talking to. When you want that scoped against real numbers, talk to us.
CTO and Co-founder at Idealogic. Directing engineering, systems architecture, security, and full-stack delivery across web, mobile, and blockchain.
Frequently asked questions
Crypto wallet app development is building the software that generates private keys, protects them, and uses them to sign blockchain transactions. The coins themselves never live in the app; they sit on a public ledger, and the wallet holds the only credential that can move them. That makes key generation, key storage, signing, chain integration and recovery the five load-bearing parts of the build. The interface matters for trust, but the key handling underneath is where the difficulty is.
Our model puts a single-chain non-custodial mobile wallet at 22 to 30 engineer-weeks, a multi-chain wallet with swaps and an on-ramp at 44 to 60, and a custodial or MPC wallet with a compliance perimeter at 90 to 120. At a blended $60 an hour, that is roughly $53,000 to $72,000, $106,000 to $144,000, and $216,000 to $288,000 respectively, before a security audit and before any licensing work. Substitute your own rate and the engineer-weeks stay the same. The two decisions that move the number most are the custody model and the chain list, and both are cheap to change in week one and expensive in month six.
Yes. A non-custodial single-chain wallet is a realistic first build for a competent mobile team, because derivation follows published standards (BIP-39, BIP-32 and BIP-44) and the device already gives you hardware-backed key storage through the Secure Enclave or the Android Keystore. Two things you shouldn't do while learning: invent your own cryptography, or hold anyone else's funds. Custody is where a side project becomes a regulated business.
A fiat eWallet, meaning a stored-value or payments app rather than a crypto wallet, lands in a similar engineering range but shifts the weight from cryptography to payment rails and compliance. You trade key management for card acquiring, ledgering, reconciliation and chargebacks, and you almost certainly need an e-money or payment licence or a sponsor who has one. Expect the compliance and integration work to dominate the budget the way key handling and audits dominate a crypto wallet build.
Build non-custodial if your users are consumers and you don't want to hold their funds, because it keeps you outside custody licensing in both the EU and the US. Build MPC when several parties or a business need to authorise transactions, or when you want account recovery without a seed phrase. Build custodial only when the product genuinely requires you to hold client assets, and price the licence, the audits and the insurance before you write a line of code.
It depends entirely on whether you control the keys, and that single question decides most of the answer. Under MiCA, providing custody and administration of crypto-assets on behalf of clients is an authorised service requiring authorisation as a crypto-asset service provider, while Recital 83 states plainly that hardware or software providers of non-custodial wallets fall outside the Regulation. In the US, FinCEN guidance FIN-2019-G001 treats hosted wallet providers as account-based money transmitters and concludes the opposite for unhosted single-signature wallet software, since the owner keeps total independent control of the value. Multi-signature providers that only add a co-signing key stay outside too. Take advice for your own jurisdiction before you build anything that touches client funds.
With three to four engineers: ten to fourteen weeks for a single-chain non-custodial wallet, sixteen to twenty-two once you add multi-chain support and swaps, and twenty-four to thirty-six for a custodial or MPC product with a compliance perimeter. Those figures assume the custody model and the chain list are frozen at kickoff. They exclude the external security audit, which you should book early because the good firms have queues.
Sometimes, and the honest test is whether the wallet is your product. For a distribution play it's usually the right trade: a branded app in weeks rather than months. The costs land later, when the vendor's chain list becomes yours and custom signing flows are limited to what the platform exposes. Build it yourself when key handling is the differentiator.
More from the journal

Custom Blockchain Development: When to Build vs Buy
Custom blockchain development means four very different jobs, from writing your own contracts on a public chain to standing up a base layer. This guide separates them, prices each route against published figures, and runs the build or buy call in order.

What Is Cryptocurrency? A Beginner's Guide to How It Works
Cryptocurrency is digital money that runs on a blockchain, not a bank. This guide explains what crypto is, how it works, the main types like Bitcoin, Ethereum, and stablecoins, how to buy and store it safely, and the risks, scams, and tax basics worth knowing first.

How Much Does Mobile App Development Cost? (2026 Guide)
There's no single price for a mobile app: a simple build and a complex one can differ tenfold. Here are the real 2026 cost ranges by complexity and platform, what actually drives the number, and how a senior team keeps it under control.