Smart Contract Audit Cost: 2026 Prices, Drivers, and Scope
Almost nobody publishes a price list for smart contract audits. This guide collects the references that do exist, dated and linked: Sherlock's 2026 bands, public contest award pools, and a vendor calculator that returns a form instead of a number. Then what moves the figure.

On this page

A smart contract audit costs between $5,000 for a simple token contract and over $250,000 for an enterprise-grade multi-chain system, with most DeFi protocol audits landing between $25,000 and $100,000. Those bands aren't ours. They come from Sherlock's market reference for 2026, published 18 February 2026, and they're close to the only bands anyone in this market publishes at all. Every serious auditor quotes privately, which is why smart contract audit cost is a question with a thousand blog answers and almost no sources behind them.
So this guide starts from the sources. Every published price reference we could open and date sits in one table below, with what each one says. After that comes the mechanics: what moves a quote, what an audit buys you, and what it demonstrably doesn't. If you came here to sanity-check a number somebody sent you, skip ahead to the tables.
The short version
- Sherlock's February 2026 reference is the closest thing to a public price list: $5,000 to $20,000 for a simple ERC-20, $40,000 to $100,000 for a mid-complexity DeFi protocol, $150,000 and up for enterprise multi-chain work, and $5,000 to $20,000 per re-audit pass.
- Public audit contests are the only part of this market with visible prices. Award pools on the seven Code4rena competitions this guide tracks ran from $18,000 to $183,500, as of 10 September 2026.
- The published "audit cost calculators" don't publish costs. Hashlock's returns a contact form and a promise of a quote.
- Scope moves the number more than line count does. Language moves it more than most founders expect: Sherlock prices Rust and Solana at a 25 to 40 percent premium over Solidity, and ZK circuits at 80 to 120 percent.
- Audits don't stop hacks on their own. CoinGecko found 88.44% of funds stolen since January 2025 came from protocols that had already been audited, and Immunefi found 89% of 2025 DeFi losses came from protocol logic, the class no scanner flags.
- Readiness is the cheapest lever you control. Every hour a reviewer spends deciphering your repository is an hour not spent finding the bug that would have cost you the treasury.
What a smart contract audit cost looks like in 2026
Two prices exist in this market. There's a wide public range, and there's the narrow one you only see after you ask. They diverge badly the moment your code stops looking like everyone else's.
The wide range is Sherlock's, quoted above. Underneath it sit tighter bands that map to recognisable scopes. A simple ERC-20 runs $5,000 to $20,000. A mid-complexity DeFi protocol runs $40,000 to $100,000, which Sherlock then translates into a realistic pre-launch budget of $60,000 to $120,000 once you count the review and the fix cycle together. Enterprise multi-chain systems start at $150,000. Re-audit passes are $5,000 to $20,000 each.
Two widely read explainer pages publish a much lower figure. Both Hedera and Chainlink's education hub say a typical audit costs $5,000 to $15,000. That's not a contradiction so much as a different question being answered. Their number describes a small standard contract reviewed by a mid-tier shop. Sherlock's describes a protocol with money in it. If your product has a treasury, an oracle and an upgrade path, budget against the second figure and treat the first as the floor for a token you could write in an afternoon.
What a smart contract audit is, and what it is not
A smart contract audit is an independent security review of on-chain code before deployment. Reviewers read the code, run tooling against it, reason about its economics, write up every finding with a severity and a fix, then verify your remediation. That's the whole product.
Three things it isn't, each of which shows up in quotes and in disappointed post-mortems.
Not a financial audit. Nobody's checking your books, your treasury policy or your token distribution. The word is borrowed and it misleads people constantly.
Not a guarantee, either. The SeedBox DeFi build we shipped runs an audit-first process, and we still say plainly in that write-up that it's a process claim, not a promise. No honest engineer calls a contract unhackable. You make the surface small, review it hard, and test it before money touches it.
And not a substitute for your own testing. It assumes it. An auditor who has to write your first fork test is billing senior review rates to do work a junior should have finished last month.
What an audit covers is a commit and a scope, which is the single most useful thing to understand about pricing. Change the code afterwards and you've changed the thing that was reviewed. For the wider picture of what threatens a deployed protocol beyond the contracts themselves, our guide to blockchain security covers the parts an audit isn't scoped to see, and DeFi smart contracts walks the build lifecycle that feeds into one.
Published smart contract audit prices, with sources and dates
We opened, verified and dated every reference below. Nothing here is inferred, averaged or rounded into a "typical" figure.
Sit with the Hashlock row for a second. A cost calculator that produces no cost is the market telling you something true: pricing here gets negotiated against a scope document, and nobody wants to be held to a number before they've seen your repository. We looked at a second vendor calculator and dropped it, because that page carried no date and the firm sells the same custom software services we do, which makes it a competitor's marketing, not a reference.
What public audit contests actually pay
Competitive audit platforms are the exception that makes the rest of the market legible. A contest has to announce its award pool to attract researchers, so the price is public before the work starts.
Source: Code4rena's public audits listing and the individual competition pages, captured 10 September 2026.
Read that as a scope ladder, not a price list. Ekubo is AMM infrastructure. K2 is a lending market spanning pooled, isolated and gated pools. Merkl at $18,000 is a smaller, tighter scope. The same site also ran mitigation reviews, the contest equivalent of a re-audit, at $4,000 for Intuition, $6,000 for Panoptic and $12,000 for Swafe, which tells you what verifying a fix is worth next to finding the bug in the first place.
One caveat before you hold a pool up against a quote. A $107,000 pool gets split among everyone who submits a valid finding, so it buys breadth of attention for a fixed window. A $107,000 private engagement buys named reviewers for a period you agree. Different products, coincidentally similar prices.
What drives smart contract audit cost
Scope drives the number. Not line count, not the feature list, and not how badly you need to launch on Thursday.
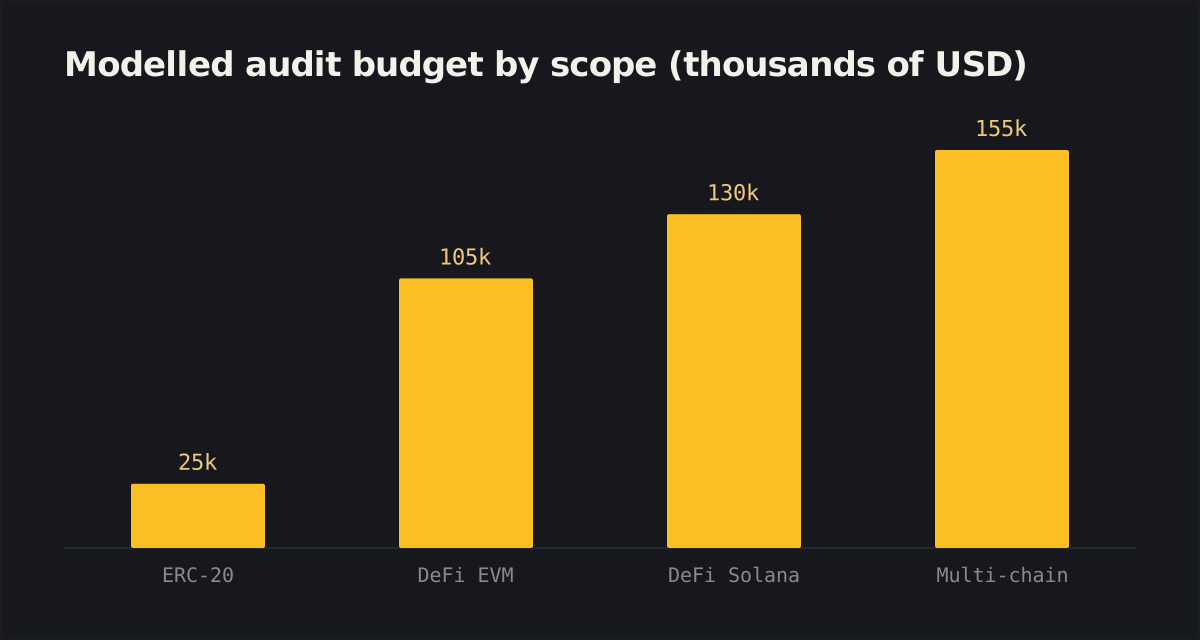
That model states its assumptions on purpose. It takes only published inputs, applies them consistently, and still spans a factor of six. Use it to see the shape of the curve, then go get a real quote.
Why novelty raises smart contract audit cost more than size does
That last row has no anchor because nobody can publish one, and it's where most of the variance lives. An ERC-20 with 400 lines is a known quantity: the reviewer has read that contract a hundred times and is looking for the three ways people get it wrong. New AMM invariant maths at 400 lines is a research problem. The auditor has to reconstruct your model, decide whether it holds under adversarial input, then decide whether your implementation matches the model. Same size, completely different job.
Everything that widens the blast radius works the same way. Each external integration is a trust assumption to trace. Each upgradeable proxy adds storage layout and initialiser risk to the surface. A cross-chain deployment multiplies the states a reviewer has to hold in their head at once. If you want the reasons those surfaces are dangerous and not merely expensive, our DeFi smart contracts guide goes through the failure modes.
The smart contract audit process, step by step

Every reputable engagement runs this shape. Knowing it is how you tell a real quote from a scan-and-invoice.
- Scope and freeze. You hand over a file list, an nSLOC count, a tagged commit and a statement of what's out of scope. Then the code stops moving. Auditing a moving target burns your budget on re-reading.
- Threat model. Reviewers write down what the system is supposed to guarantee, who's trusted with what, and where value can leave. If your team hasn't done this already, the auditor does it on your dime, at their rate.
- Automated analysis. Slither, Trail of Bits' Solidity and Vyper static analysis framework, ships roughly a hundred detectors. Aderyn does the same job in Rust with editor integration. Echidna fuzzes against properties you declare, and Foundry's invariant testing throws random call sequences at your contracts, 256 runs at a depth of 100 calls by default. This stage clears the noise, nothing more.
- Manual review. Humans read the code, reason about the economics, and try to compose legitimate calls into an exploit. This is the part you're paying for.
- Report and severity classification. Every finding gets a severity, a description and a recommended fix. The common mistake here is arguing severity down instead of arguing the finding out.
- Fix window and re-audit. You remediate, they verify. A fix can introduce a new bug, which is why the pass is priced separately, and why skipping it is false economy.
What a smart contract audit report contains
A report ranks findings by severity against a named methodology, and that methodology should be in the document. If it isn't, ask which one they use before you sign.
Immunefi's Vulnerability Severity Classification System v2.3 is the most widely referenced public scale. It defines impacts, not adjectives, which is what makes it arguable in good faith.
Payout column: the ENS programme on Immunefi, captured 10 September 2026. Programme caps vary. The severity definitions don't.
Contest platforms compress the same scale. Code4rena's severity categorization uses three bands: High, where "assets can be stolen/lost/compromised directly", Medium, where assets are not at direct risk "but the function of the protocol or its availability could be impacted", and QA, which absorbs low-risk and centralisation findings. Fewer bands, less argument, and a deliberate discouragement of informational noise.
Read a sample report before you sign anything. The severity table tells you how they think, and the informational findings tell you how carefully they read.
Do you still need a manual smart contract audit
Yes, and the loss data makes the case more sharply than any auditor's pitch does.
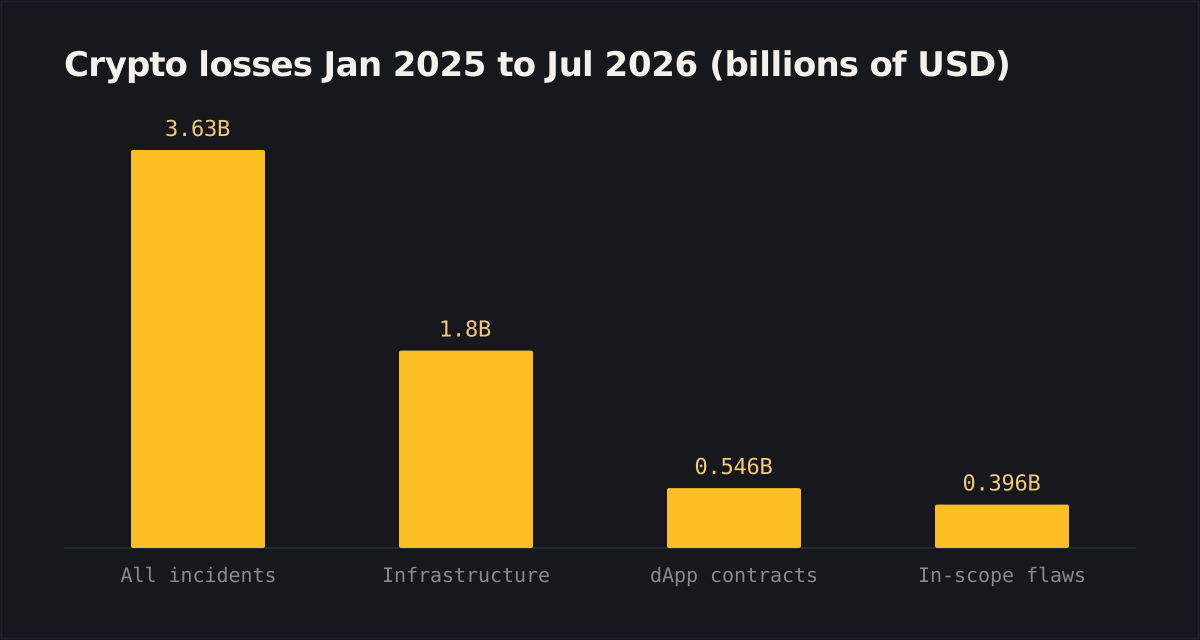
Start with the uncomfortable number. CoinGecko counted $3.63 billion lost across 245 documented incidents between January 2025 and July 2026, and 147 of those incidents hit protocols that had been audited before they were compromised, which works out to 88.44% of the capital drained. Read carelessly, that's an argument against audits. It isn't. Bigger systems get audited and bigger systems get attacked, so the audited share of losses tracks the audited share of value.
The second cut of the same dataset is the one that should change your budget. Only about 11.0% of those incidents involved in-scope smart contract flaws, worth $396.0 million. Infrastructure and supply chain breaches took over $1.8 billion. Front ends, build pipelines, dependency compromises and key management are where the money mostly leaves, and a contract audit isn't scoped to any of them.
So where does manual review still earn its fee? On the class of bug that has no signature. Immunefi's six-year study of DeFi loss data, published 27 April 2026, found that 89% of 2025 DeFi protocol losses came from protocol logic exploits, while the pattern-matchable categories collapsed: bridge incidents fell from 73% of losses in 2022 to 3% in 2025, and ecosystem-class attacks such as flash-loan oracle manipulation went from roughly 19% to under 1%. Tooling and shared knowledge killed the templated attacks. What's left is bespoke logic, and bespoke logic needs a person.
Cetus is the example to keep in mind when a vendor implies AI review has closed that gap. In May 2025 an overflow check in the AMM's maths library let an attacker mint enormous liquidity positions for almost nothing, draining over $200 million. Dedaub's post-mortem records that "audits to this version of the AMM by Ottersec and MoveBit do not find this issue", and that a further Zellic audit in April 2025 "found no issues beyond informational findings". Three firms, one shift operation, $200 million.
The practical conclusion isn't to buy more audit. It's to stop treating the audit as the whole security budget. Sherlock's reference puts annual security spend for protocols with meaningful TVL at $150,000 to $500,000, and an audit is one line inside that.
How to lower smart contract audit cost without lowering the bar
You can't negotiate a good auditor's rate down by much. You can absolutely change how many hours they need, and readiness is the whole lever.
The invariants line is the one that pays
If you do one thing on that list, write down your invariants and encode them. Foundry's invariant runner will hammer them with random call sequences long before an auditor sees the repository, and every violation it surfaces is a finding you didn't pay for. It also changes the conversation. Instead of "here's the code, tell us what breaks", you're saying "here's what we believe must hold, tell us where we're wrong". Far cheaper question to answer.
Two more levers. Timeline is the one founders give away for free, and Sherlock prices urgency at a 20 to 40 percent premium, so booking the slot a month out is a real discount. Scope reduction is legitimate when it's honest: pulling a peripheral contract out of review because it holds no value and has no privileged calls is fine. Pulling it out because the quote came back high is how you end up with an exploit in the part nobody read.
How to read an audit quote and what to ask an auditor
A quote worth taking seriously names the commit, the file list, the nSLOC in scope, the number of reviewer-weeks, the reviewers themselves, and what a re-audit pass costs. If it names only a lump sum and a start date, you're being sold a report.
Questions that change what you learn, in the order we ask them:
- Who is actually on this? Firms sell brand and staff the work. Ask for names, then ask what else those people are reviewing that fortnight.
- What have you audited that resembles this? Domain track record beats general reputation. A team fluent in lending liquidations isn't automatically fluent in ZK circuits.
- Can we see a full report from a comparable engagement? Not the summary. The whole document, informational findings included.
- What's in scope, stated as files? And confirm what's explicitly out.
- How many reviewer-weeks, and is one re-audit pass included? This is the question that turns a lump sum into something comparable.
- What happens if we disagree on a severity? The answer tells you whether their methodology is a document or a mood.
- What will you not find? An auditor who answers that one honestly beats one who doesn't.
Choosing a smart contract auditor
The market splits into three shapes, and most teams moving real value use more than one.
Private audit firms give you named reviewers, a fixed fee, an NDA, and a report you control the release of. Trail of Bits maintains Slither and Echidna as public tooling, and OpenZeppelin maintains the contract libraries most of the industry builds on. That's a form of track record you can inspect for yourself.
Competitive platforms such as Code4rena, Sherlock and Cantina post your scope publicly for a fixed window and split an announced pool among the researchers who find something. You trade confidentiality for breadth. The pools above are what that breadth costs.
Bug bounties such as Immunefi run continuously after launch and price by impact rather than by time, which is the only model that keeps paying attention to a live system. An audit is a snapshot. A bounty is a subscription.
How to check an audit report is real
Two checks catch most of the theatre. Ask for the report as a public link on the auditor's own domain, then verify that the commit hash in it matches the deployed, verified contract on a block explorer. A report about a commit that was never deployed protects nobody. If a project shows you a badge instead of a document, treat the badge as marketing.
For a longer look at evaluating a build partner instead of a reviewer, we cover the vendor question in choosing a DeFi development company and keep a working shortlist in our overview of blockchain development companies.
One disclosure, because this is a real conflict of interest otherwise. Idealogic doesn't sell audits. We write and prepare code for them, and we commission third-party auditors on behalf of clients. On SeedBox that meant Solidity contracts written, reviewed and tested before funds were involved, on a build that ran from the idea stage through to a live MVP with individual wallets and token-holder governance. On Planetcoin, a card-to-crypto exchange with KYC and AML obligations, the same discipline applied to a mostly off-chain surface. Both are process claims. Neither is a certification, and we don't present them as one.
Where this leaves your smart contract audit budget
Smart contract audit cost is knowable within a factor of two before you talk to anyone, and unknowable within a factor of five if you skip the scope work. The published bands give you the outer walls: $5,000 to $20,000 for a token, $40,000 to $120,000 for a DeFi protocol you intend to launch, $150,000 and up if it spans chains, plus $5,000 to $20,000 for each re-audit pass and a premium of 25 to 120 percent for anything that isn't Solidity on an EVM.
Where you land inside those walls depends on how much reasoning your code demands and how much of the preparatory work you've already done. That second half is yours. Freeze the commit, write the invariants, run the free tools, hand over a scope document, and the same money buys deeper review.
Keep the audit in proportion, though. The loss data says most of the money leaves through infrastructure, not through contract logic, so a clean report is a floor rather than a finish line. If you're still weighing an on-chain build in the first place, custom versus ready-made blockchain and our guides to web3 development, creating a cryptocurrency, decentralized exchange development and a tokenization platform cover the decisions that set your audit scope long before anyone quotes on it. Our blockchain development team builds to that standard on every engagement: small surfaces, written invariants, external review, and verified fixes before mainnet.
CTO and Co-founder at Idealogic. Directing engineering, systems architecture, security, and full-stack delivery across web, mobile, and blockchain.
Frequently asked questions
Sherlock's February 2026 market reference puts the range at $5,000 for a simple token contract to over $250,000 for an enterprise-grade multi-chain system, with most DeFi protocol audits between $25,000 and $100,000 and a simple ERC-20 between $5,000 and $20,000. Hedera and Chainlink both publish a narrower $5,000 to $15,000 for a typical contract, which describes a small standard scope, not protocol work. No auditor publishes a rate card, so treat every one of these as a band to check your quote against, not a price you can order at. If your product holds a treasury, budget against Sherlock's numbers.
There's no dated salary series worth citing, but the payout side is public. Code4rena lists the full award pool of every competition it runs; among the seven contests this guide tracks, pools ran from $18,000 to $183,500 as of 10 September 2026, split among everyone who filed a valid finding. Bug bounties publish per-finding tiers instead: on the ENS programme, which uses Immunefi's severity system, a critical finding pays up to $250,000 and a low pays a flat $2,500.
Yes, and the loss data says so twice over. Immunefi's April 2026 study of six years of DeFi losses found that 89% of 2025 DeFi protocol losses came from protocol logic exploits, which is exactly the class scanners can't see. And the Cetus overflow bug that drained over $200 million in May 2025 sat in code three separate firms had reviewed. Tooling and contests shorten the review. They don't replace the person reasoning about your economics.
Scope decides it. Sherlock's published anchors tie roughly 500 nSLOC to a 3-day review window, 3,000 nSLOC to 18 days and 6,000 nSLOC to 38 days, and those windows sit before the fix-and-re-review loop and don't include it. Add one to two weeks for your team to fix findings and the auditor to verify them. Book early: good firms and contest slots are scheduled weeks ahead, and Sherlock prices urgency at a 20 to 40 percent premium.
An independent security review of on-chain code before it's deployed. Reviewers read the code, run static analysis and fuzzing against it, reason about the economics, and deliver findings ranked by severity, followed by a re-review of your fixes. It isn't a financial audit and it isn't a guarantee.
Because an audit covers one commit and one scope, and attackers don't. CoinGecko's 2026 State of Crypto Security Report counted $3.63 billion lost across 245 incidents between January 2025 and July 2026, and 147 of those incidents hit protocols that had been audited first, representing 88.44% of the money taken. The part that should change your budget: the same report found only about 11.0% of incidents involved in-scope smart contract flaws. Most of the money left through infrastructure and supply chain, which no contract audit is scoped to cover.
Sherlock publishes $5,000 to $20,000 per pass. Contest platforms price the same step openly: Code4rena ran mitigation reviews at $4,000, $6,000 and $12,000 in the window we captured, against original pools many times larger. Budget for at least one. A fix can introduce a new bug.
A private audit gives you named reviewers, a fixed fee, an NDA and a report you control. A contest posts your code publicly for a fixed window and splits an announced award pool among everyone who finds something, so you're buying breadth of attention instead of a specific reviewer's calendar. Contests publish their pools, which is why they're the only part of this market with visible prices. Most teams moving real money run both, then a bounty afterwards.
More from the journal

Decentralized Exchange Development: Architecture and Cost
A build guide for decentralized exchange development: how AMM, order-book and intent designs differ, what the architecture really contains, what a fork costs you in licence terms, and a cost model with its assumptions written down.

Top 10 Blockchain Development Companies in 2026, Compared
Ten blockchain development companies whose work you can check yourself, plus the verification tests that separate an engineering firm from a reseller, what engagements cost, and what blockchain IoT projects have to solve that ordinary dApps never face.

How to Create a Cryptocurrency: Coins, Tokens & Costs
Creating a cryptocurrency is three different projects wearing the same name. This guide separates them: a token on an existing chain, your own appchain, or a no-code launcher. With a working ERC-20, the 2026 rulebook in the EU and the US, and a costed model of each route.